

Get ready to pass the AZ-700 Exam right now using our Microsoft Certification Exam Package
A fully updated 2021 AZ-700 Exam Dumps exam guide from training expert Test4Cram
NEW QUESTION 21
You are configuring two network virtual appliances (NVAs) in an Azure virtual network. The NVAs will be used to inspect all the traffic within the virtual network.
You need to provide high availability for the NVAs. The solution must minimize administrative effort. What should you include in the solution?
- A. Azure Standard Load Balancer
- B. Azure Front Door
- C. Azure Application Gateway
- D. Azure Traffic Manager
Answer: C
NEW QUESTION 22
You have an Azure subscription that is linked to an Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com. The subscription contains the following resources:
* An Azure App Service app named App1
* An Azure DNS zone named contoso.com
* An Azure private DNS zone named private.contoso.com
* A virtual network named Vnet1
You create a private endpoint for App1. The record for the endpoint is registered automatically in Azure DNS.
You need to provide a developer with the name that is registered in Azure DNS for the private endpoint.
What should you provide?
- A. app1.contoso.onmicrosoft.com
- B. app1.contoso.com
- C. app1.private.contoso.com
- D. app1.privatelink.azurewebsites.net
Answer: D
NEW QUESTION 23
You have an Azure virtual network that contains the subnets shown in the following table.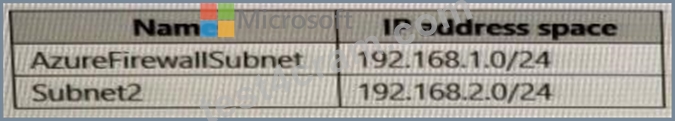
You deploy an Azure firewall to AzureFirewallSubnet. You route all traffic from Subnet2 through the firewall.
You need to ensure that all the hosts on Subnet2 can access an external site located at https://*.contoso.com.
What should you do?
- A. In a firewall policy, create a DNAT rule.
- B. In a firewall policy, create a network rule.
- C. In a firewall policy, create an application rule.
- D. Create a network security group (NSG) and associate the NSG to Subnet2.
Answer: D
NEW QUESTION 24
You have an application named App1 that listens for incoming requests on a preconfigured group of 50 TCP ports and UDP ports.
You install App1 on 10 Azure virtual machines.
You need to implement load balancing for App1 across all the virtual machines. The solution must minimize the number of load balancing rules.
What should you include in the solution?
- A. Azure Application Gateway v2 that has multiple site hosting enabled
- B. Azure Standard Load Balancer that has high availability (HA) ports enabled
- C. Azure Application Gateway V2 that has multiple listeners
- D. Azure Standard Load Balancer that has Floating IP enabled
Answer: D
NEW QUESTION 25
You have the Azure environment shown in the exhibit.
You have virtual network peering between Vnet1 and Vnet2. You have virtual network peering between Vnet4 and Vnet5. The virtual network peering is configured as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 26
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that contains the following resources:
* A virtual network named Vnet1
* A subnet named Subnet1 in Vnet1
* A virtual machine named VM1 that connects to Subnet1
* Three storage accounts named storage1, storage2. and storage3
You need to ensure that VM1 can access storage1. VM1 must be prevented from accessing any other storage accounts.
Solution: You create a network security group (NSG). You configure a service tag for MicrosoftStorage and link the tag to Subnet1.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 27
You have an Azure subscription that contains a single virtual network and a virtual network gateway.
You need to ensure that administrators can use Point-to-Site (P2S) VPN connections to access resources in the virtual network. The connections must be authenticated by Azure Active Directory (Azure AD).
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 28
You need to connect Vnet2 and Vnet3. The solution must meet the virtual networking requirements and the business requirements.
Which two actions should you include in the solution? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. On the peering from Vnet1, select Allow gateway transit.
- B. On the peerings from Vnet2 and Vnet3, select Allow gateway transit.
- C. On the peering from Vnet1, select Allow forwarded traffic.
- D. On the peering from Vnet1, select Use remote gateways.
- E. On the peerings from Vnet2 and Vnet3, select Use remote gateways.
Answer: A,C
Explanation:
Topic 1, Litware. Inc Case Study 1
Overview
Litware. Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 10 devices.
Existing Environment:
Hybrid Environment
The on-prernises network contains an Active Directory forest named litwareinc.com that syncs to an Azure Active Directory (Azure AD) tenant named litwareinc.com by usinq Azure AD Connect.
All the offices connect to a virtual network named Vnetl by using a Site-to-Site VPN connection.
Azure Environment
Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Azure AD tenant. Sub1 contains resources in the East US Azure region as shown in the following table.
There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.
Requirements:
Business Requirements
Litware wants to minimize costs whenever possible, as long as all other requirements are met.
Virtual Networking Requirements
Litware identifies the following virtual networking requirements:
* Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
* Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
* Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
* Minimize the size of the subnets allocated to platform-managed services.
* Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.
Hybrid Networking Requirements
Litware identifies the following hybrid networking requirements:
* Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely.
Connections must be authenticated by Azure AD.
* Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
* The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
* Traffic between Vnet2 and Vnet3 must be routed through Vnet1.
PaaS Networking Requirements
Litware identifies the following networking requirements for platform as a service (PaaS):
* The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
* The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.
NEW QUESTION 29
You fail to establish a Site-to-Site VPN connection between your company's main office and an Azure virtual network.
You need to troubleshoot what prevents you from establishing the IPsec tunnel.
Which diagnostic log should you review?
- A. TunnelDiagnosticLog
- B. IKEDiagnosticLog
- C. RouteDiagnosticLog
- D. GatewayDiagnosticLog
Answer: D
NEW QUESTION 30
You have an Azure application gateway named AppGW1 that balances requests to a web app named App1.
You need to modify the server variables in the response header of App1.
What should you configure on AppGW1?
- A. rewrites
- B. HTTP settings
- C. listeners
- D. rules
Answer: B
NEW QUESTION 31
You have an Azure application gateway for a web app named App1. The application gateway allows end-to-end encryption.
You configure the listener for HTTPS by uploading an enterprise signed certificate.
You need to ensure that the application gateway can provide end-to-end encryption for App1. What should you do?
- A. Upload the public key certificate to the HTTP settings.
- B. Set Listener type to Multi site.
- C. Increase the Unhealthy threshold setting in the custom probe.
- D. Enable the SSL profile for the listener.
Answer: D
NEW QUESTION 32
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that contains the following resources:
* A virtual network named Vnet1
* A subnet named Subnet1 in Vnet1
* A virtual machine named VM1 that connects to Subnet1
* Three storage accounts named storage1, storage2, and storage3
You need to ensure that VM1 can access storage1. VM1 must be prevented from accessing any other storage accounts.
Solution: You configure the firewall on storage1 to only accept connections from Vnet1.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 33
In which NSGs can you use ASG1 and to which virtual machine network interfaces can you associate ASG1?
To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 34
You have an Azure application gateway named AppGW1 that provides access to the following hosts:
* www.adatum.com
* www.contoso.com
* www.fabrikam.com
AppGW1 has the listeners shown in the following table.
You create Azure Web Application Firewall (WAF) policies for AppGW1 as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 35
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that contains the following resources:
* A virtual network named Vnet1
* A subnet named Subnet1 in Vnet1
* A virtual machine named VM1 that connects to Subnet1
* Three storage accounts named storage1, storage2, and storage3
You need to ensure that VM1 can access storage1. VM1 must be prevented from accessing any other storage accounts.
Solution: You create a network security group (NSG) and associate the NSG to Subnet1.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 36
You have an Azure subscription that contains the resources shown in the following table.
The IP Addresses settings for Vnet1 are configured as shown in the exhibit.
You need to ensure that you can integrate WebApp1 and Vnet1.
Which three actions should you perform in sequence before you can integrate WebApp1 and Vnet1? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
NEW QUESTION 37
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure application gateway that has Azure Web Application Firewall (WAF) enabled.
You configure the application gateway to direct traffic to the URL of the application gateway.
You attempt to access the URL and receive an HTTP 403 error. You view the diagnostics log and discover the following error.
You need to ensure that the URL is accessible through the application gateway.
Solution: You disable the WAF rule that has a ruleld of 920300.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 38
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure application gateway that has Azure Web Application Firewall (WAF) enabled.
You configure the application gateway to direct traffic to the URL of the application gateway.
You attempt to access the URL and receive an HTTP 403 error. You view the diagnostics log and discover the following error.
You need to ensure that the URL is accessible through the application gateway.
Solution: You configure a custom cookie and an exclusion rule.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 39
You have an Azure Virtual Desktop deployment that has 500 session hosts.
All outbound traffic to the internet uses a NAT gateway.
During peak business hours, some users report that they cannot access internet resources. In Azure Monitor, you discover many failed SNAT connections.
You need to increase the available SNAT connections.
What should you do?
- A. Add a public IP address.
- B. Bind the NAT gateway to another subnet.
- C. Deploy Azure Standard Load Balancer that has outbound rules.
Answer: A
NEW QUESTION 40
You are planning an Azure Point-to-Site (P2S) VPN that will use OpenVPN.
Users will authenticate by using an on premises Active Directory domain.
Which additional service should you deploy to support the VPN authentication?
- A. a certification authority (CA)
- B. an Azure key vault
- C. a RADIUS server
- D. Azure Active Directory (Azure AD) Application Proxy
Answer: D
NEW QUESTION 41
You need to prepare Vnet1 for the deployment of an ExpressRoute gateway. The solution must meet the hybrid connectivity requirements and the business requirements.
Which three actions should you perform in sequence for Vnet1? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
NEW QUESTION 42
You are implementing the virtual network requirements for VM Analyze.
What should you include in a custom route that is linked to Subnet2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 43
You have the hybrid network shown in the Network Diagram exhibit.
You have a peering connection between Vnet1 and Vnet2 as shown in the Peering-Vnet1-Vnet2 exhibit.
You have a peering connection between Vnet1 and Vnet3 as shown in the Peering -Vnet1-Vnet3 exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 44
......
Master 2021 Latest The Questions Microsoft Certification and Pass AZ-700 Real Exam!: https://www.test4cram.com/AZ-700_real-exam-dumps.html
Practice To AZ-700 - Test4Cram Remarkable Practice On your Designing and Implementing Microsoft Azure Networking Solutions Exam: https://drive.google.com/open?id=1bus_MFf6RHr3GzWcBwmEIXEhOu7tfOw_