

Juniper JN0-231 Questions and Answers Guarantee you Oass the Test Easily
Share Latest JN0-231 DUMP with 107 Questions and Answers
Click on the link below for getting more info about the Juniper JN0-231 Exam:
Official link to the Juniper JN0-231 Exam
NEW QUESTION # 54
Which two statements are correct about the integrated user firewall feature?(Choose two.)
- A. It maps IP addresses to individual users.
- B. It supports IPv4 addresses.
- C. It allows tracking of non-Windows Active Directory users.
- D. It uses the LDAP protocol.
Answer: A,C
NEW QUESTION # 55
What is the default timeout value for TCP sessions on an SRX Series device?
- A. 30 seconds
- B. 60 minutes
- C. 60 seconds
- D. 30 minutes
Answer: D
Explanation:
By default, TCP has a 30-minute idle timeout, and UDP has a 60-second idle timeout. Additionally, known IP protocols have a 30-minute timeout, whereas unknown ones have a 60-second timeout. Setting the inactivity timeout is very useful, particularly if you are concerned about applications either timing out or remaining idle for too long and filling up the session table. According to the Juniper SRX Series Services Guide, this can be configured using the 'timeout inactive' statement for the security policy.
NEW QUESTION # 56
Click the Exhibit button.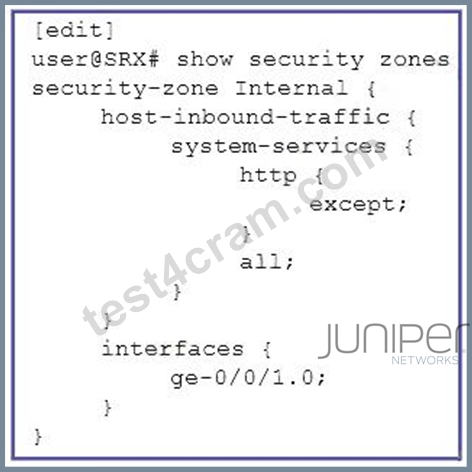
What is the purpose of the host-inbound-traffic configuration shown in the exhibit?
- A. to permit all host inbound traffic on the internal security zone, but deny HTTP traffic
- B. to deny and log all host inbound traffic on the internal security zone, except for HTTP traffic
- C. to permit host inbound HTTP traffic and deny all other traffic on the internal security zone
- D. to permit host inbound HTTP traffic on the internal security zone
Answer: A
NEW QUESTION # 57
A security zone is configured with the source IP address 192.168.0.12/255.255.0.255 wildcard match.
In this scenario, which two IP packets will match the criteria? (Choose two.)
- A. 192.168.22.12
- B. 192.168.1.21
- C. 192.168.1.12
- D. 192.168.0.1
Answer: A,C
NEW QUESTION # 58
When configuring antispam, where do you apply any local lists that are configured?
- A. advanced security policy
- B. custom objects
- C. antispam feature-profile
- D. antispam UTM policy
Answer: B
Explanation:
user@host# set security utm custom-objects url-pattern url-pattern-name https://www.juniper.net/documentation/us/en/software/junos/utm/topics/topic-map/security-local-list-antispam-filtering.html
NEW QUESTION # 59
Which Juniper ATP feed provides a dynamic list of known botnet servers and known sources of malware downloads?
- A. C&C cloud feed
- B. blocklist feed
- C. Geo IP feed
- D. infected host cloud feed
Answer: D
NEW QUESTION # 60
Which three operating systems are supported for installing and running Juniper Secure Connect client software? (Choose three.)
- A. Windows 10
- B. Android
- C. Windows 7
- D. Linux
- E. macOS
Answer: A,C,E
Explanation:
Juniper Secure Connect client software is supported on the following three operating systems: Windows 7, Windows 10, and macOS. For more information, please refer to the Juniper Secure Connect Administrator Guide, which can be found on Juniper's website. The guide states: "The Juniper Secure Connect client is supported on Windows 7, Windows 10, and macOS." It also provides detailed instructions on how to install and configure the software for each of these operating systems.
NEW QUESTION # 61
What is a type of security feed that Sky ATP provides to a vSRX series device by default?
- A. ACL feeds
- B. C&C feeds
- C. Malware feeds
- D. RSS feeds
Answer: B
NEW QUESTION # 62
What must you do first to use the Monitor/Alarms/Policy Log workspace in J-Web?
- A. You must enable logging that uses the SD-Syslog format.
- B. You must enable security logging that uses the TLS transport mode.
- C. You must enable stream mode security logging on the SRX Series device.
- D. You must enable event mode security logging on the SRX Series device.
Answer: D
NEW QUESTION # 63
On an SRX device, you want to regulate traffic base on network segments.
In this scenario, what do you configure to accomplish this task?
- A. Zones
- B. NAT
- C. Screens
- D. ALGs
Answer: A
NEW QUESTION # 64
What does IPsec use to negotiate encryption algorithms?
- A. IKE
- B. ESP
- C. TLS
- D. AH
Answer: B
NEW QUESTION # 65
Which Juniper Networks solution uses static and dynamic analysis to search for day-zero malware threats?
- A. IPS
- B. UTM
- C. Juniper ATP Cloud
- D. firewall filters
Answer: C
Explanation:
Malware Sandboxing
Detect and stop zero-day and commodity malware within web, email, data center, and application traffic targeted for Windows, Mac, and IoT devices. https://www.juniper.net/us/en/products/security/advanced-threat-prevention.html
NEW QUESTION # 66
Screens on an SRX Series device protect against which two types of threats? (Choose two.)
- A. malicious e-mail attachments
- B. IP spoofing
- C. zero-day outbreaks
- D. ICMP flooding
Answer: B,D
NEW QUESTION # 67
You want to deploy a NAT solution.
In this scenario, which solution would provide a static translation without PAT?
- A. pool-based NAT without PAT
- B. pool-based NAT with address shifting
- C. pool-based NAT with PAT
- D. interface-based source NAT
Answer: B
Explanation:
Translation of the original source IP address to an IP address from a user-defined address pool by shifting the IP addresses. This type of translation is one-to-one, static, and without port address translation. If the original source IP address range is larger than the IP address range in the user-defined pool, untranslated packets are dropped. https://www.juniper.net/documentation/us/en/software/junos/nat/topics/topic-map/nat-security-source-and-source-pool.html
NEW QUESTION # 68
Which two criteria should a zone-based security policy include? (Choose two.)
- A. zone context
- B. a destination port
- C. an action
- D. a source port
Answer: B,D
Explanation:
A security policy is a set of statements that controls traffic from a specified source to a specified destination using a specified service. A policy permits, denies, or tunnels specified types of traffic unidirectionally between two points.
Each policy consists of:
A unique name for the policy.
A from-zone and a to-zone, for example: user@host# set security policies from-zone untrust to-zone untrust A set of match criteria defining the conditions that must be satisfied to apply the policy rule. The match criteria are based on a source IP address, destination IP address, and applications. The user identity firewall provides greater granularity by including an additional tuple, source-identity, as part of the policy statement.
A set of actions to be performed in case of a match-permit, deny, or reject.
Accounting and auditing elements-counting, logging, or structured system logging.
https://www.juniper.net/documentation/us/en/software/junos/security-policies/topics/topic-map/security-policy-configuration.html
NEW QUESTION # 69
Which two actions are performed on an incoming packet matching an existing session? (Choose two.)
- A. Zone processing
- B. Service ALG processing
- C. Security policy evolution
- D. Screens processing
Answer: B,D
NEW QUESTION # 70
Which statement about service objects is correct?
- A. All applications in service objects are not available on the vSRX Series device.
- B. All applications are custom defined by the administrator.
- C. All applications are either custom or Junos defined.
- D. All applications are predefined by Junos.
Answer: C
Explanation:
"Service objects represent applications and services that can be assigned to a security policy rule. Applications and services can either be predefined by Junos software or custom defined by the administrator." Reference:
Juniper Networks JNCIA-SEC Exam Guide: https://www.juniper.net/training/certification/certification-exam-guides/jncia-sec-exam-guide/
NEW QUESTION # 71
Which two statements are correct about functional zones? (Choose two.)
- A. A function is used for special purpose, such as management interface
- B. A functional zone uses security policies to enforce rules for transit traffic.
- C. Functional zones separate groups of users based on their function.
- D. Traffic received on the management interface in the functional zone cannot transit out other interface.
Answer: A,D
NEW QUESTION # 72
Which two criteria should a zone-based security policy include? (Choose two.)
- A. zone context
- B. a source port
- C. a destination port
- D. an action
Answer: C,D
NEW QUESTION # 73
You are monitoring an SRX Series device that has the factory-default configuration applied.
In this scenario, where are log messages sent by default?
- A. Junos Space Log Director
- B. to a local log file named messages
- C. to a local syslog server on the management network
- D. Junos Space Security Director
Answer: C
NEW QUESTION # 74
You want to enable the minimum Juniper ATP services on a branch SRX Series device.
In this scenario, what are two requirements to accomplish this task? (Choose two.)
- A. Configure the juniper-atp user account on the branch device.
- B. Register for a Juniper ATP account on https://sky.junipersecurity.net.
- C. Execute the Juniper ATP script on the branch device.
- D. Install a basic Juniper ATP license on the branch device.
Answer: B,D
NEW QUESTION # 75
Which Statement is correct about Sky ATP?
- A. Sky ATP can provide live threat feeds to SRX series devices
- B. The local Sky ATP platform downloads the latest threat from managed site
- C. Sky ATP relies on the SRX series device to open and analyze suspect file attachments
- D. Sky ATP is a local hardware-based security threat analyzer that performs multiple tasks.
Answer: A
NEW QUESTION # 76
......
The JN0-231 exam is designed to validate the skills and knowledge of candidates in various aspects of network security, including security protocols, security policies, firewall filters, intrusion detection and prevention, and security management. Candidates who pass JN0-231 exam are able to demonstrate a comprehensive understanding of these concepts, which is essential for any network security professional.
The JN0-231 exam is a multiple-choice exam that consists of 65 questions. Candidates have 90 minutes to complete the exam. JN0-231 exam is available in several languages, including English, Japanese, Simplified Chinese, and Korean. Successful candidates will receive the Juniper Networks Certified Associate - Security (JNCIA-SEC) certification, which is a valuable credential for individuals who want to prove their skills and knowledge in Juniper Networks security solutions.
Dumps for Free JN0-231 Practice Exam Questions: https://www.test4cram.com/JN0-231_real-exam-dumps.html
PDF Dumps 2025 Exam Questions with Practice Test: https://drive.google.com/open?id=1Qr4_bHCskGXsvUT8om-3O8n6UkuAaLHp