

[Sep 12, 2022] New Microsoft MS-500 Dumps with Test Engine and PDF (New Questions)
Pass Your MS-500 Exam Easily - Real MS-500 Practice Dump Updated
Microsoft MS-500 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
NEW QUESTION 32
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
You create and enforce an Azure AD Identity Protection sign-in risk policy that has the following settings:
* Assignments: Include Group1, Exclude Group2
* Conditions: Sign in risk of Low and above
* Access: Allow access, Require password multi-factor authentication
You need to identify how the policy affects User1 and User2.
What occurs when each user signs in from an anonymous IP address? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation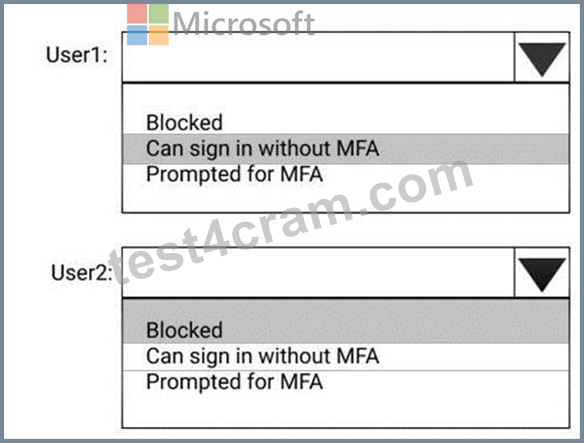
NEW QUESTION 33
あなたの会社はMicrosoft AzureのAdvanced Threat Protection(ATP)を使用しています。
Sensor1という名前のAzure ATPセンサーに対する更新の遅延展開を有効にします。
Azure ATPクラウドサービスが更新されてからSensor1が更新されるまでの期間
- A. 1時間
- B. 12時間
- C. 24時間
- D. 48時間
- E. 7日
Answer: C
Explanation:
説明/参照:
Explanation:
注:遅延期間は24時間でした。 ATPリリース2.62では、24時間の遅延期間が延長されました
72時間まで。
NEW QUESTION 34
You have a Microsoft 365 E5 subscription and a hybrid Microsoft Exchange Server organization.
Each member of a group named Executive has an on-premises mailbox. Only the Executive group members have multi-factor authentication (MFA) enabled. Each member of a group named Research has a mailbox in Exchange Online.
You need to use Microsoft Office 365 Attack simulator to model a spear-phishing attack that targets the Research group members.
The email addresses that you intend to spoof belong to the Executive group members.
What should you do first?
- A. Migrate the Executive group members to Exchange Online
- B. From the Azure ATP admin center, configure the primary workspace settings
- C. From the Microsoft Azure portal, configure the user risk policy settings in Azure AD Identity Protection
- D. Enable MFA for the Research group members
Answer: D
Explanation:
Explanation/Reference:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/attack-simulator
NEW QUESTION 35
You need to configure threat detection for Active Directory. The solution must meet the security requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: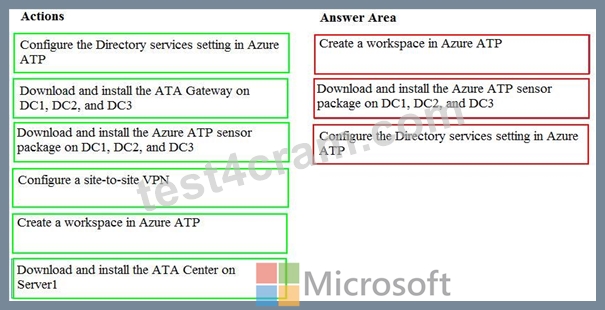
Topic 3, Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, and New York.
The company has the offices shown in the following table.
Contoso has IT, human resources (HR), legal, marketing, and finance departments. Contoso uses Microsoft 365.
Existing Environment
Infrastructure
The network contains an Active Directory domain named contoso.com that is synced to a Microsoft Azure Active Directory (Azure AD) tenant. Password writeback is enabled.
The domain contains servers that run Windows Server 2016. The domain contains laptops and desktop computers that run Windows 10 Enterprise.
Each client computer has a single volume.
Each office connects to the Internet by using a NAT device. The offices have the IP addresses shown in the following table.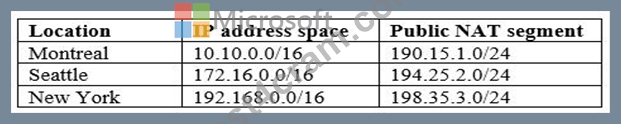
Named locations are defined in Azure AD as shown in the following table.
From the Multi-Factor Authentication page, an address space of 198.35.3.0/24 is defined in the trusted IPs list.
Azure Multi-Factor Authentication (MFA) is enabled for the users in the finance department.
The tenant contains the users shown in the following table.
The tenant contains the groups shown in the following table.
Customer Lockbox is enabled in Microsoft 365.
Microsoft Intune Configuration
The devices enrolled in Intune are configured as shown in the following table.
The device compliance policies in Intune are configured as shown in the following table.
The device compliance policies have the assignments shown in the following table.
The Mark devices with no compliance policy assigned as setting is set to Compliant.
Requirements
Technical Requirements
Contoso identifies the following technical requirements:
* Use the principle of least privilege
* Enable User1 to assign the Reports reader role to users
* Ensure that User6 approves Customer Lockbox requests as quickly as possible
* Ensure that User9 can implement Azure AD Privileged Identity Management
NEW QUESTION 36
You have a Microsoft 365 subscription that uses a default domain name of fabrikam.com.
You create a safe links policy, as shown in the following exhibit.
Which URL can a user safely access from Microsoft Word Online?
- A. fabrikam.phishing.fabrikam.com
- B. www.malware.fabrikam.com
- C. malware.fabrikam.com
- D. fabrikam.contoso.com
Answer: B
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/set-up-a-custom-blocked-urls-list-wtih-atp
NEW QUESTION 37
You configure Microsoft Azure Active Directory (Azure AD) Connect as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: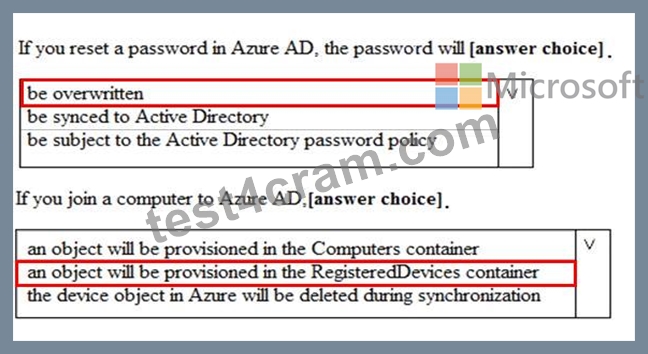
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-device-writeback
NEW QUESTION 38
You need to recommend a solution for the user administrators that meets the security requirements for auditing.
Which blade should you recommend using from the Azure Active Directory admin center?
- A. Azure AD Identity Protection
- B. Access review
- C. Authentication methods
- D. Sign-ins
Answer: D
Explanation:
References:
https://docs.microsoft.com/en-us/azure/active-directory/reports-monitoring/concept-sign-ins
NEW QUESTION 39
You have multiple Microsoft 365 subscriptions.
You need to build an application that will retrieve the Microsoft Secure Score data of each subscription.
What should you use?
- A. the Microsoft Graph Security API
- B. the Azure Monitor REST API
- C. the Microsoft Office 365 Management API
- D. the Microsoft Defender for Endpoint API
Answer: C
NEW QUESTION 40
You view Compliance Manager as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/meet-data-protection-and-regulatory-reqs-using-microsoft-cloud
NEW QUESTION 41
Your company has a Microsoft 365 subscription that contains the users shown in the following table.
The company implements Windows Defender Advanced Threat Protection (Windows Defender ATP).
Windows Defender ATP includes the roles shown in the following table: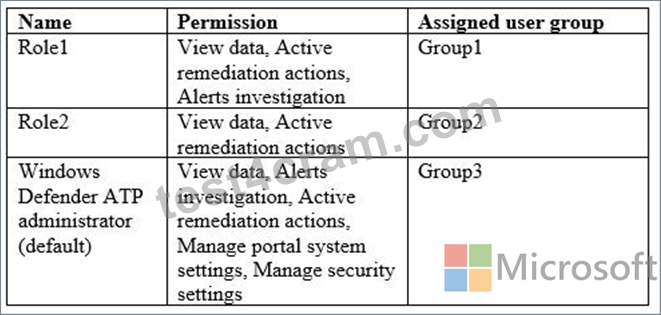
Windows Defender ATP contains the machine groups shown in the following table:
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 42
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
You add internal as a blocked word in the group naming policy for contoso.com.
You add Contoso- as prefix in the group naming policy for contoso.com.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/solutions/groups-naming-policy?view=o365-worldwide
NEW QUESTION 43
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains 1,000 user mailboxes.
An administrator named Admin1 must be able to search for the name of a competing company in the mailbox of a user named User5.
You need to ensure that Admin1 can search the mailbox of User5 successfully. The solution must prevent Admin1 from sending email messages as User5.
Solution: You assign the eDiscovery Manager role to Admin1, and then create a eDiscovery case.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/exchange/policy-and-compliance/ediscovery/ediscovery?view=exchserver-
2019
NEW QUESTION 44
You have a Microsoft 365 subscription. From the Security & Compliance admin center, you create the retention policies shown in the following table.
Policy1 if configured as showing in the following exhibit.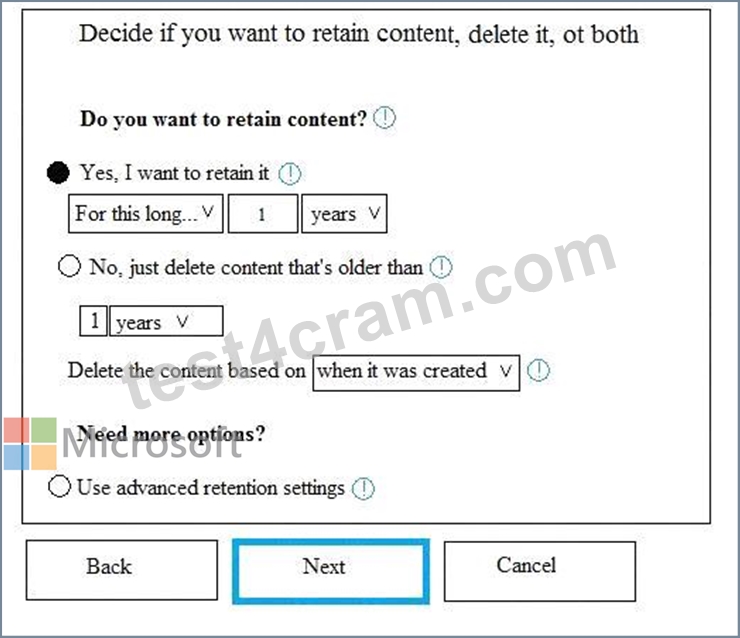
Policy2 is configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.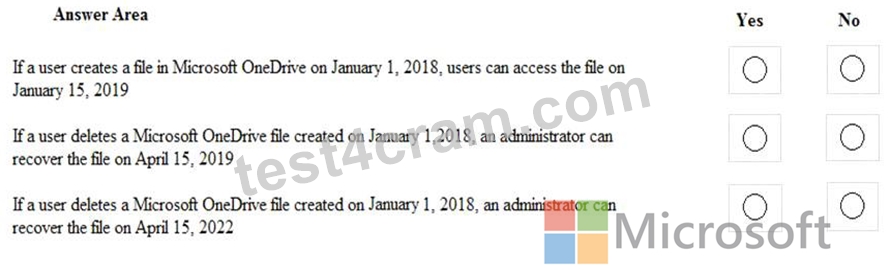
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/retention-policies?redirectSourcePath=%252fen-
NEW QUESTION 45
You have a Microsoft 365 subscription that uses a default name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/onedrive/manage-sharing
NEW QUESTION 46
You have a Microsoft 365 subscription that uses a default name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/onedrive/manage-sharing
NEW QUESTION 47
You are evaluating which devices are compliant in Intune.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 48
You have a Microsoft 365 subscription.
You need to create data loss prevention (DLP) queries in Microsoft SharePoint Online to find sensitive data stored in sites.
Which type of site collection should you create first?
- A. Document Center
- B. eDiscovery Center
- C. Records Center
- D. Enterprise Search Center
Answer: B
Explanation:
Explanation/Reference:
https://support.office.com/en-us/article/overview-of-data-loss-prevention-in-sharepoint-server-2016-80f907bb- b944-448d-b83d-8fec4abcc24c
NEW QUESTION 49
Microsoft 365テナントがあります。
Windows 10を実行している500台のコンピューターがあります。
Windows Defender Advanced Threat Protection(Windows)を使用してコンピューターを監視することを計画している
コンピューターがMicrosoft Intuneに登録された後のDefender ATP)。
コンピュータがWindows Defender ATPに接続されていることを確認する必要があります。
Windows Defender ATP用にIntuneをどのように準備する必要がありますか?
- A. 条件付きアクセスポリシーを作成します
- B. 登録制限を設定します
- C. Windowsオートパイロット展開プロファイルを作成します
- D. デバイス設定プロファイルを作成します
Answer: D
Explanation:
説明/参照:
参照:
https://docs.microsoft.com/en-us/intune/advanced-threat-protection
NEW QUESTION 50
You have a Microsoft 365 subscription that include three users named User1, User2, and User3.
A file named File1.docx is stored in Microsoft OneDrive. An automated process updates File1.docx every minute.
You create an alert policy named Policy1 as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation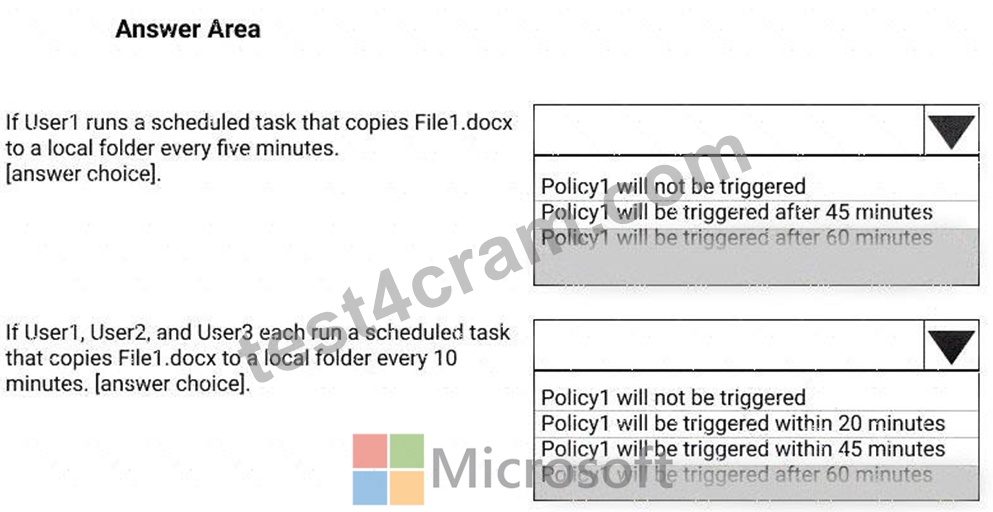
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/alert-policies
NEW QUESTION 51
......
What Are the Career Opportunities and Their Salary Scale?
A professional who has succeeded in MS-500 exam and has earned the Microsoft 365 Certified: Security Administrator Associate certificate can secure well paying jobs that require knowledge of cloud technologies like those services offered by Microsoft 365 managed by Azure.
How to Start Reviewing the Microsoft MS-500 Exam
Get the exam guide for Microsoft MS-500 Exam
Microsoft MS-500 Exam: Tips to survive if you don't have time to read all the pages
The MS-500 is a certification exam that tests skills and knowledge of Windows Server 2012 R2. The MS-500 has replaced the Microsoft Certified Systems Engineer (MCSE) as a new certification level in IT focused on IT Pros rather than systems engineers. There is no official date for when this will happen, but the writing's been on the wall for quite some time. This test engine is officially approved by Microsoft for this certification level. In this article, I will give you an overview of what to expect from the exam, how to prepare for it, and a brief introduction of the exam & its format that can help you build your skills up before taking it. I will also give you the idea of MS-500 Dumps which you can use for the preparation of the exam. Studying from this material is a good way to be more confident before taking the exam.
Test4Cram just published the Microsoft MS-500 exam dumps!: https://www.test4cram.com/MS-500_real-exam-dumps.html
For your comfort, Test4Cram provides you the convenience of free Microsoft 365 braindumps demo: https://drive.google.com/open?id=1NOrIc51HWnOMXXkONwfunc3i769rz-dy