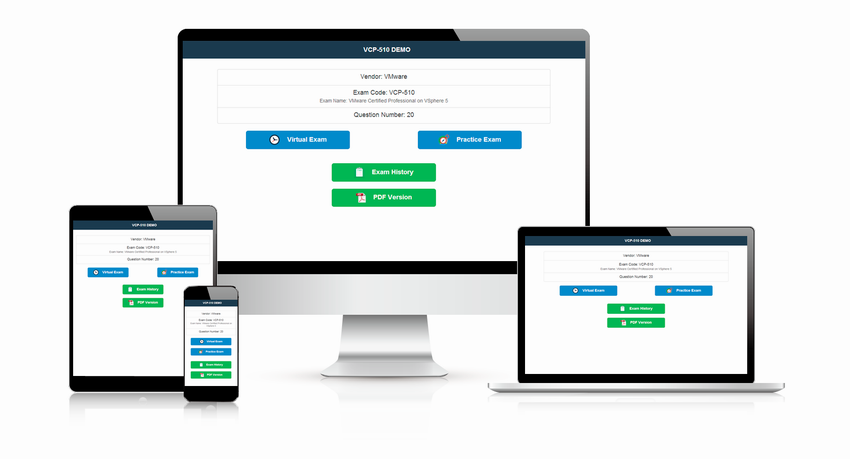
No Wi-Fi is no excuse. Practice once online, and the Test4Cram materials travel offline — the printable PDF and the Windows engine hold your 144 practice questions wherever the network does not reach.
Splunk SPLK-5001 Exam Overview:
| Certification Vendor: | Splunk |
|---|---|
| Exam Name: | Splunk Certified Cybersecurity Defense Analyst |
| Exam Number: | SPLK-5001 |
| Exam Price: | $200 USD |
| Passing Score: | 700 (on a 0-1000 scale) |
| Exam Duration: | 90 minutes |
| Certificate Validity Period: | 3 years |
| Available Languages: | English |
| Real Exam Qty: | 100 |
| Exam Format: | Multiple-choice (single answer), Multiple-choice (multiple answers), Hands-on lab scenarios |
| Related Certifications: | Splunk Core Certified Power User Splunk Enterprise Security Certified Admin Splunk Core Certified User |
| Sample Questions: |  |
| Exam Way: | Pearson VUE testing centers (onsite only; online proctoring not available for this exam) |
| Pre Condition: | Splunk Core Certified Power User is strongly recommended before attempting SPLK-5001. Splunk Enterprise Security Admin experience is highly beneficial. |
| Official Syllabus URL: | https://www.splunk.com/en_us/training/certification/splunk-certified-cybersecurity-defense-analyst.html |
Splunk SPLK-5001 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Splunk Enterprise Security (ES) Fundamentals | 15-20% | - ES Architecture and Components
|
| Threat Intelligence Integration | 10-15% | - Threat Artifacts Management
|
| Asset-Based Detection Tactics | 10-15% | - Behavioral Baselines and Profiling
|
| Splunk Search Processing Language (SPL) for Security | 20-25% | - Security-Specific SPL Patterns
|
| Advanced Content Development | 15-20% | - Correlation Search Development
|
| Enterprise Security Administration | 10-15% | - ES Configuration and Tuning
|
| Incident Investigation and Response | 15-20% | - Investigation Workflow
|
SPLK-5001 Exam FAQ — Convenience, Quality, Policy
The official Splunk Certified Cybersecurity Defense Analyst outline defines 7 domains. The leading three are Splunk Enterprise Security (ES) Fundamentals (15-20%), Asset-Based Detection Tactics (10-15%), and Splunk Search Processing Language (SPL) for Security (20-25%). The full list is in the topics section above, and Test4Cram's 144 practice questions cover each one.
Splunk Core Certified Power User is strongly recommended before attempting SPLK-5001. Splunk Enterprise Security Admin experience is highly beneficial. Since requirements change over time, confirm the latest on the official Splunk exam page before scheduling.
The Splunk Certified Cybersecurity Defense Analyst exam contains 100 to complete within 90 minutes. Timed simulation in the Test4Cram Desktop Test Engine teaches that rhythm before exam day does.
Splunk recommends these training resources for the Splunk Certified Cybersecurity Defense Analyst exam:
Follow the training with steady self-testing — the 144 practice questions from Test4Cram help you apply theory and fill any gaps the training leaves.
Test4Cram issues a full refund if you take the Splunk Certified Cybersecurity Defense Analyst exam within 60 days of purchase and do not pass. The policy does not apply if the exam is taken within 3 days of purchase, if the exam was never actually taken, or to free materials or expired orders, and the candidate name must match the payer name. Submit a scan of your enrollment slip and the official Score Report PDF within 2 days of the exam; claims are processed within 7 days. Alternatively, exchange for two free exam products of equal value and keep your original update service. Orders arrive by email within 1 minute — contact support if nothing arrives within 2 hours.
Three versions of the same study materials: a printable, expert-prepared PDF with free demo download and instant access; a Desktop Test Engine for Windows with customizable simulation and timed modes that works offline; and an Online Test Engine for any browser on Windows, Mac, Android, and iOS with test history and performance review — not limited to any equipment, and friendly even without a network. All 144 practice questions are identical across versions. Every purchase includes 365 days of free updates, a 50% renewal discount afterward, and unlimited computer installations.
The SPLK-5001 exam is a Splunk certification exam validating the Splunk Certified Cybersecurity Defense Analyst syllabus shown above. It belongs to these credential paths: Splunk Core Certified User, Splunk Core Certified Power User, Splunk Enterprise Security Certified Admin. Candidates in 2026 start with Test4Cram's 144 practice questions, available as a printable PDF, a Windows Desktop Test Engine, and an Online Test Engine — three versions of the same materials.
The Splunk Certified Cybersecurity Defense Analyst exam requires 700 (on a 0-1000 scale) to pass, and registration costs $200 USD. A failed attempt means paying the same fee again — a readiness check with the Test4Cram engines before booking is the cheaper option.
Pearson VUE testing centers (onsite only; online proctoring not available for this exam) Register for the Splunk Certified Cybersecurity Defense Analyst exam through these official channels:
After booking, Test4Cram delivers your practice questions within 1 minute — preparation starts the same day.
Splunk Certified Cybersecurity Defense Analyst Sample Questions:
The Security Operations team would like to track improvements after customizing dashboards to help analysts triage security alerts more efficiently. Which metric would they use?
- A. Mean Time to Detect
- B. Mean Time to Respond
- C. Recovery Time
- D. Dwell Time
Correct Answer: A 🗳️
Explanation: Only visible for Test4Cram members. You can sign-up / login (it's free).
Which of the following is a best practice when creating performant searches within Splunk?
- A. Utilize the transaction command to aggregate data for faster analysis.
- B. Utilize multiple wildcards across fields to ensure returned data is complete and available.
- C. Utilize specific fields to return only the data that is required.
- D. Utilize Aggregating commands to ensure all data is available prior to Streaming commands.
Correct Answer: C 🗳️
Which of the following are correct statements about Splunk Enterprise Security annotations?
- A. Annotations can be used to mark notable events in the investigation.
- B. Annotations are applied automatically to all incoming data.
- C. Annotations are used for visual representation only and do not affect search results.
- D. Annotations help enrich data with additional information.
Correct Answer: A,D 🗳️
What do frameworks and standards help accomplish in the cybersecurity landscape?
- A. Promote isolation between security teams.
- B. Decrease the number of data sources.
- C. Create new vulnerabilities.
- D. Improve interoperability and consistency.
Correct Answer: D 🗳️
An analyst discovers she has only raw data from a source. She believes that it could be of great value to future analysis efforts if it were available to existing correlation searches and reports.
What process should the analyst suggest be performed for that source?
- A. Data ingest evaluation via Splunk Enterprise.
- B. Asset and Identity evaluation via Splunk Enterprise Security.
- C. Data ingestion via Splunk Security Essentials.
- D. Common Information Model normalization via a Splunk Add-On.
Correct Answer: D 🗳️
Explanation: Only visible for Test4Cram members. You can sign-up / login (it's free).
Viewing page 1 out of 29 pages.
Viewing questions 1-5 out of 144 questions.