

[Apr-2026] FCP_GCS_AD-7.6 exam torrent Fortinet study guide
Use Valid New FCP_GCS_AD-7.6 Test Notes & FCP_GCS_AD-7.6 Valid Exam Guide
Fortinet FCP_GCS_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
| Topic 12 |
|
| Topic 13 |
|
| Topic 14 |
|
| Topic 15 |
|
| Topic 16 |
|
| Topic 17 |
|
| Topic 18 |
|
| Topic 19 |
|
| Topic 20 |
|
NEW QUESTION # 20
Which Fortinet proprietary protocol do you use when deploying an active-passive high-availability (HA) cluster in Google Cloud?
- A. Unicast FGCP
- B. Broadcast FGCP
- C. Multicast FGSP
- D. Anycast FGSP
Answer: A
Explanation:
Unicast FGCP (FortiGate Clustering Protocol) is the proprietary protocol used for active-passive HA clusters in Google Cloud, enabling state synchronization and failover communication between cluster members.
NEW QUESTION # 21
Your organization has deployed an active-active high-availability (HA) FortiGate cluster in Google Cloud.
You have noticed a significant increase in asymmetrical traffic flow.
Which two actions can you take to mitigate the issue? (Choose two.)
- A. Enable symmetric hashing on the external load balancer.
- B. Enable destination NAT for ingress traffic.
- C. Enable the layer 3 unified threat management (UTM) scanning feature if the FortiGate devices are on ForiOS 6.4 or later.
- D. Enable source NAT for ingress traffic.
Answer: A,D
Explanation:
Enabling source NAT ensures consistent source IPs, promoting symmetric traffic flow.
Symmetric hashing on the load balancer helps distribute traffic flows evenly and consistently across cluster members, reducing asymmetric routing.
NEW QUESTION # 22
Which architecture inspection type in Google Cloud is most closely associated with Google Cloud Interconnect?
- A. Inbound north-south traffic inspection
- B. Outbound north-south traffic inspection
- C. Hybrid cloud inspection
- D. East-west traffic inspection
Answer: C
Explanation:
Google Cloud Interconnect connects on-premises networks with Google Cloud, enabling hybrid cloud environments. Inspection related to this connectivity focuses on hybrid cloud traffic flows.
NEW QUESTION # 23
An administrator is tasked to deploy two FortiGate devices in two different zoned to achieve geographical redundancy.
Which two architectural considerations must the administrator address? (Choose two.)
- A. The FortiGate devices can be deployed in the same subnet.
- B. The FortiGate devices must be deployed in two different regions.
- C. The FortiGate devices cannot be assigned the second IP address in the subnets that they are deployed in.
- D. The FortiGate devices must not be deployed in the same VPC.
Answer: B,C
Explanation:
Deploying FortiGate devices in different regions ensures geographic redundancy.
The second IP address in a subnet is reserved for the default gateway in Google Cloud, so FortiGate devices cannot use that IP.
NEW QUESTION # 24
Refer to the exhibit.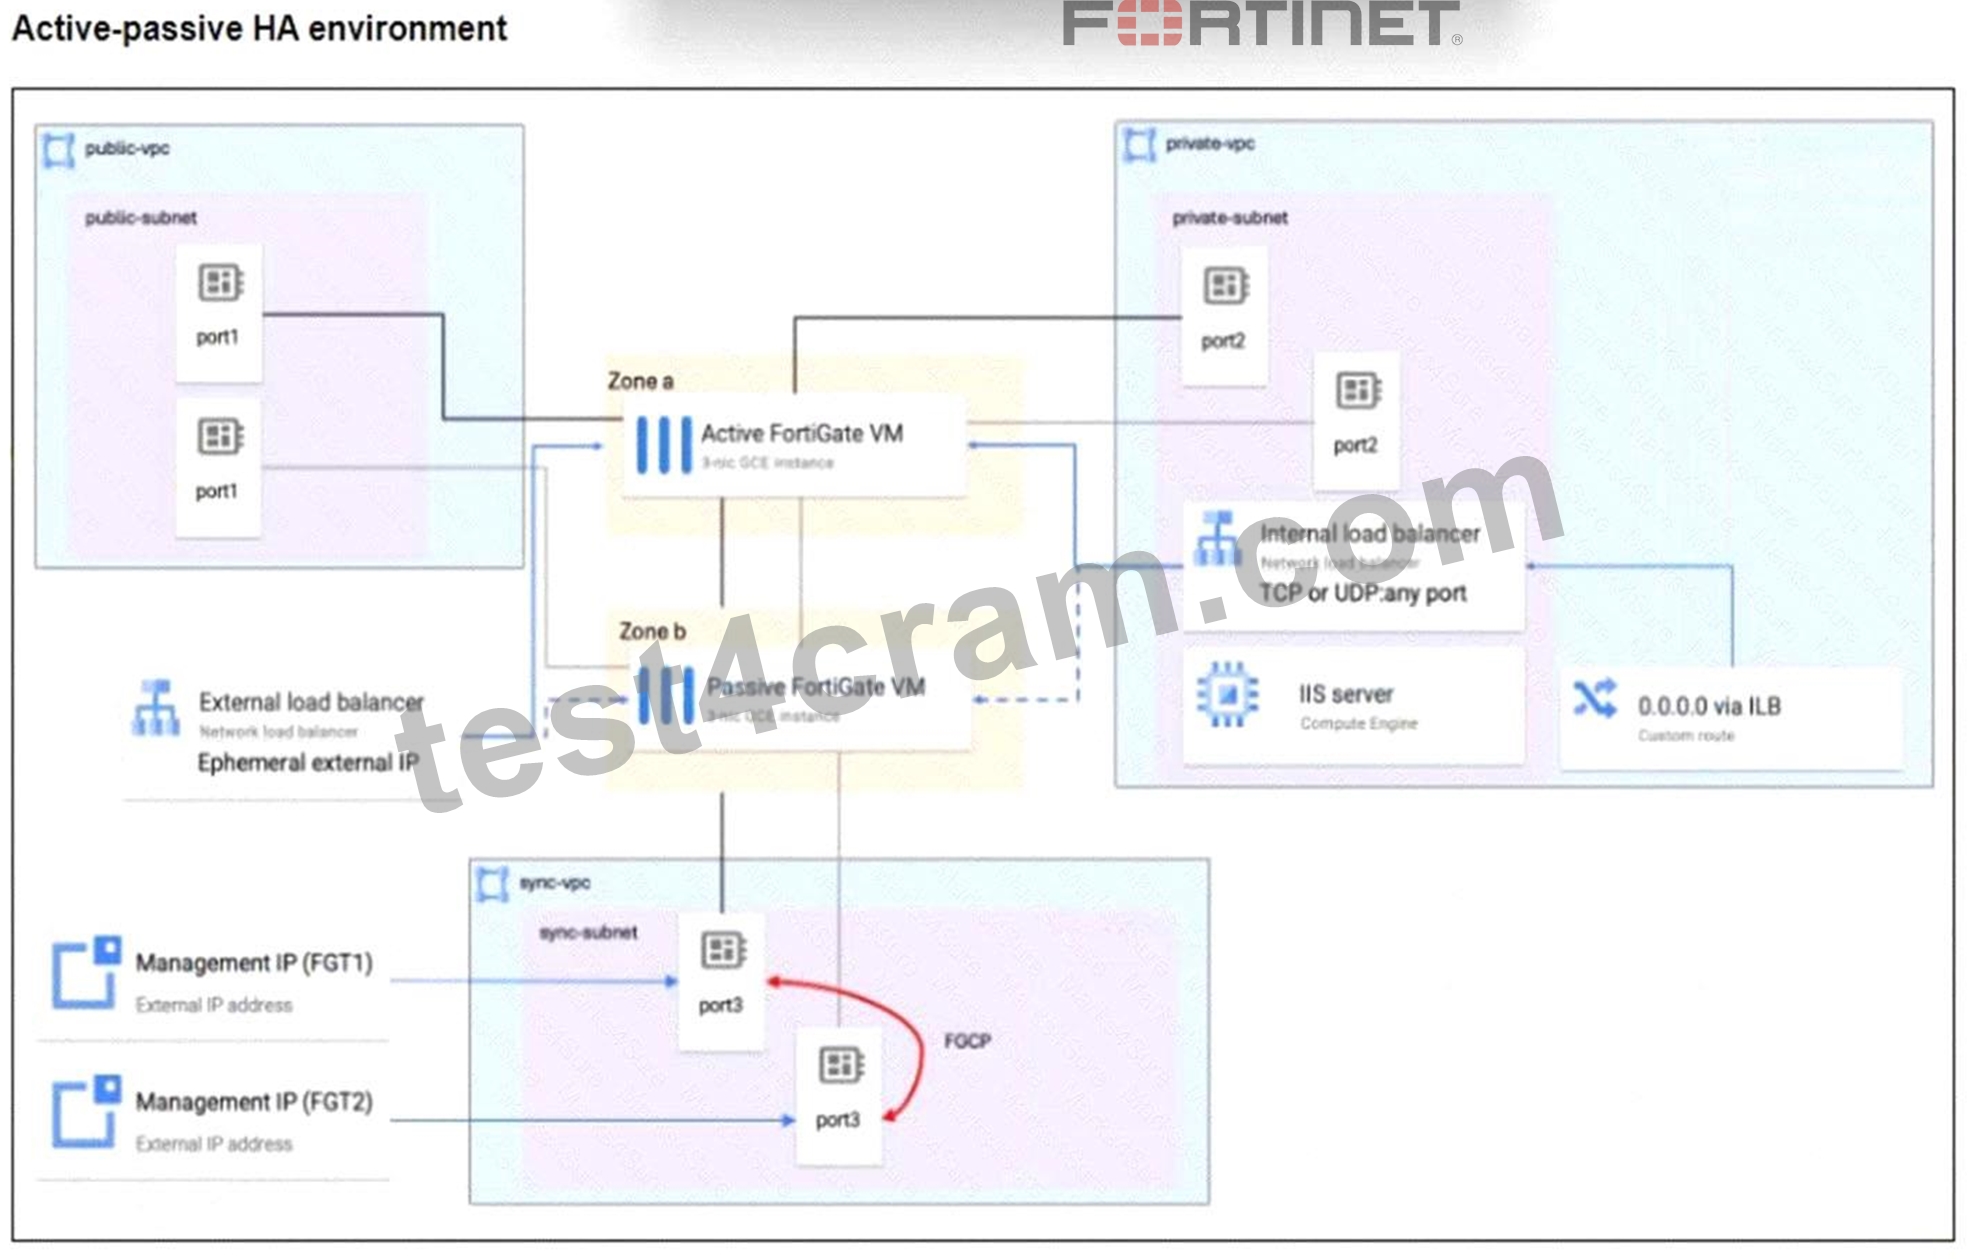
Which three things happen during a failover in which the passive FortiGate VM becomes the master cluster member in an active-passive high-availability (HA) environment? (Choose three.)
- A. The Management IP address moves from port3 of the current active member to port3 of the new active cluster member.
- B. The custom route is updated using API calls to forward all traffic to port2 of the new active cluster member device.
- C. The health check for the passthrough load balancers forces internal traffic to route to port2 of the new active cluster member.
- D. The health check ensures that incoming traffic to the ephemeral external IP address of the load balancer is forwarded to the new active cluster member.
- E. The health check status will indicate that the old active cluster member is unhealthy.
Answer: B,D,E
Explanation:
The load balancer health check detects the failure of the old active member and forwards traffic to the new active member.
The health check reflects the status change, marking the previous active as unhealthy.
API calls update custom routes to redirect traffic to the new active cluster member's internal interface (port2).
NEW QUESTION # 25
Refer to the exhibit.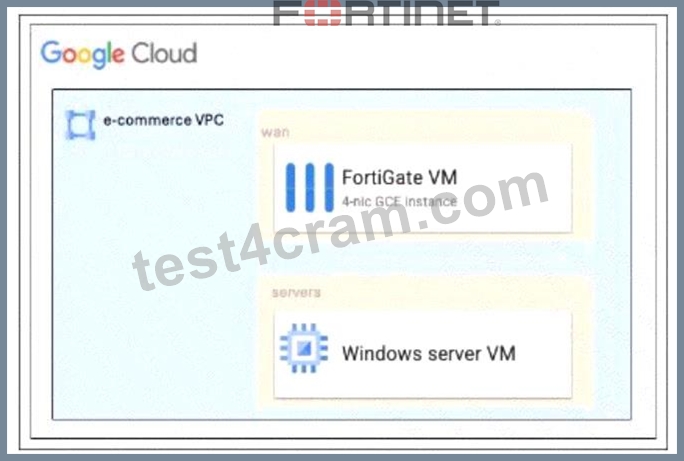
An administrator is troubleshooting network connectivity issues between two VMs deployed in Google Cloud.
One VM is a FortiGate located in the subnet "wan" that is part of the VPC "e-commerce". The other VM is a Windows server located in subnet "servers", which is also in the "e-commerce" VPC.
What are two reasons you cannot pint the Windows server from FortiGate? (Choose two.)
- A. The default Google Cloud firewall policy does not allow this traffic.
- B. ICMP traffic is blocked between Google Cloud subnets by default.
- C. The Windows firewall is blocking the traffic.
- D. Add a Google Cloud firewall rule to allow ICMP traffic inbound to the Windows firewall VM.
Answer: C,D
Explanation:
Google Cloud firewall rules are stateful and, by default, do not allow ICMP traffic; you must explicitly allow ICMP inbound traffic to the Windows VM.
The Windows VM's own firewall might block ICMP traffic, preventing ping responses.
NEW QUESTION # 26
You have been tasked with deploying an active-active FortiGate high-availability cluster in Google Cloud.
How can you ensure that traffic will flow symmetrically?
- A. There is no need to ensure traffic symmetry because FortiGate can effectively inspect asymmetric traffic.
- B. Enable the layer 3 unified threat management scanning feature on FortiGate.
- C. Deploy internal passthrough network load balancers on both sides of the cluster they support symmetric hashing.
- D. Google Cloud performs NAT on incoming traffic for external passthrough network load balancers. No action is needed.
Answer: C
NEW QUESTION # 27
Refer to the exhibit.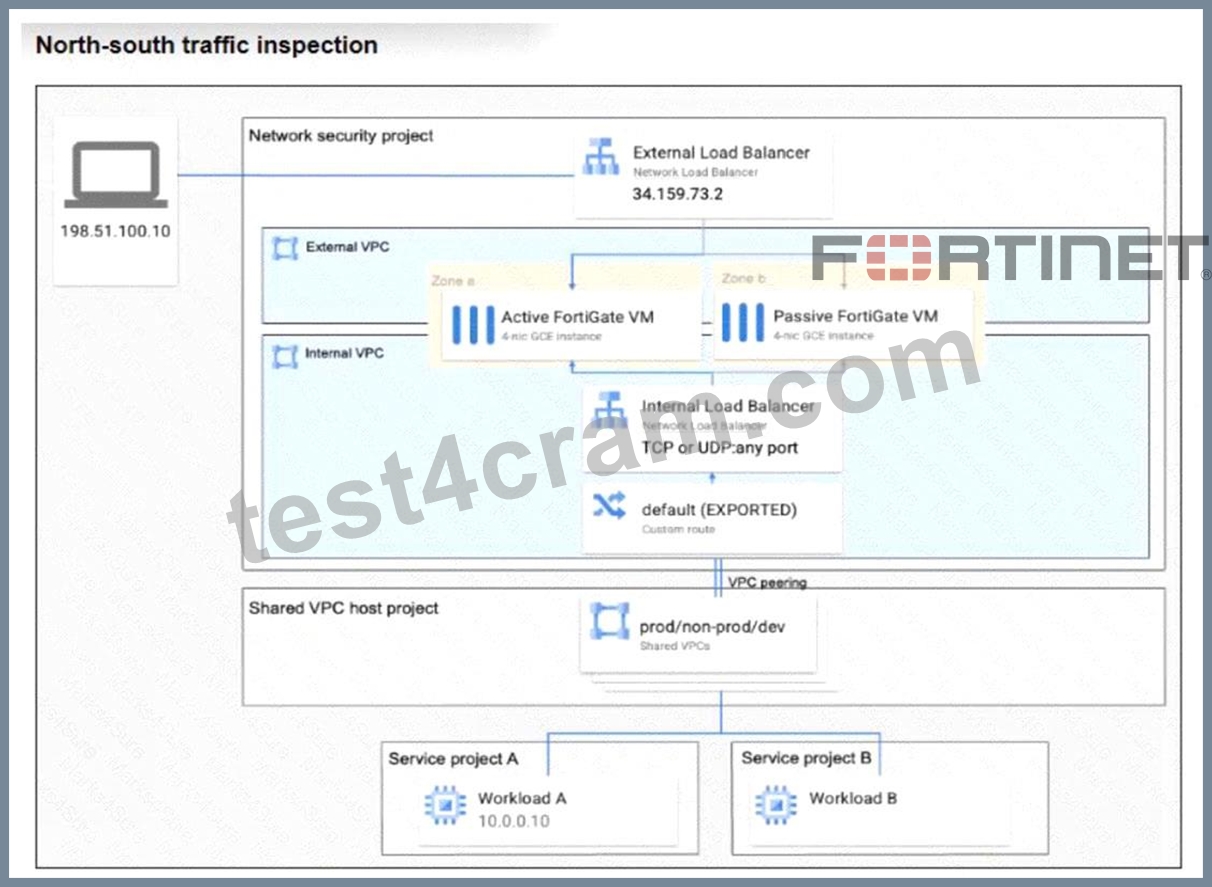
Which two types of traffic flow must the FortiGate cluster inspect, if the client at 198.51.100.10 sends traffic to the Workload A instance? (Choose two.)
- A. West-bound
- B. North-bound
- C. South-bound
- D. East-bound
Answer: C,D
Explanation:
South-bound traffic refers to traffic coming from outside the network (the client 198.51.100.10) into the internal environment.
East-bound traffic refers to traffic moving laterally within the internal network, such as between VPCs or workloads, which the FortiGate cluster can inspect for internal threats.
NEW QUESTION # 28
Google Cloud network services offer vast functionality and inter-connectivity between the cloud and on- premises networks.
Which three additional functions does FortiGate offer when deployed in Google Cloud to complement the native services offered by Google Cloud? (Choose three.)
- A. Secure SD-WAN with application visibility
- B. Web filtering
- C. SSL VPN
- D. SSL inspection
- E. OSPF over IPSec
Answer: A,C,D
Explanation:
FortiGate provides SSL VPN capabilities for secure remote access.
It offers SSL inspection to decrypt and inspect encrypted traffic for threats.
FortiGate supports Secure SD-WAN with deep application visibility and control, enhancing network performance and security beyond native Google Cloud services.
NEW QUESTION # 29
For what three reasons must you deploy a set of Google Cloud passthrough network load balancers for an active-passive high-availability (HA) FortiGate cluster instead of a set of Google Cloud proxy network load balancers? (Choose three.)
- A. Passthrough network load balancers can forward all protocols.
- B. Passthrough network load balancers support health checks.
- C. Passthrough network load balancers terminate SSL connections.
- D. Passthrough network load balancers offer the highest throughput.
- E. Passthrough network load balancers rely on API calls from FortiGate devices during HA failovers.
Answer: A,B,D
Explanation:
Passthrough load balancers support health checks to monitor backend health for failover.
They can forward all protocols, not limited to HTTP/HTTPS like proxy load balancers.
Passthrough load balancers provide higher throughput because they don't terminate sessions.
NEW QUESTION # 30
Your organization has decided to deploy a high-availability (HA) cluster. One kye requirement of the deployment is to support configuration synchronization.
Which three deployment types should be considered? (Choose three.)
- A. Active-passive HA using FGSP
- B. Active-active HA using auto scaling
- C. Active-passive HA using software-defined networking (SDN)
- D. Active-passive HA using passthrough load balancers
Answer: A,C,D
Explanation:
These three deployment types support configuration synchronization between HA cluster members, which is critical for maintaining consistent state and seamless failover.
NEW QUESTION # 31
Refer to the exhibit.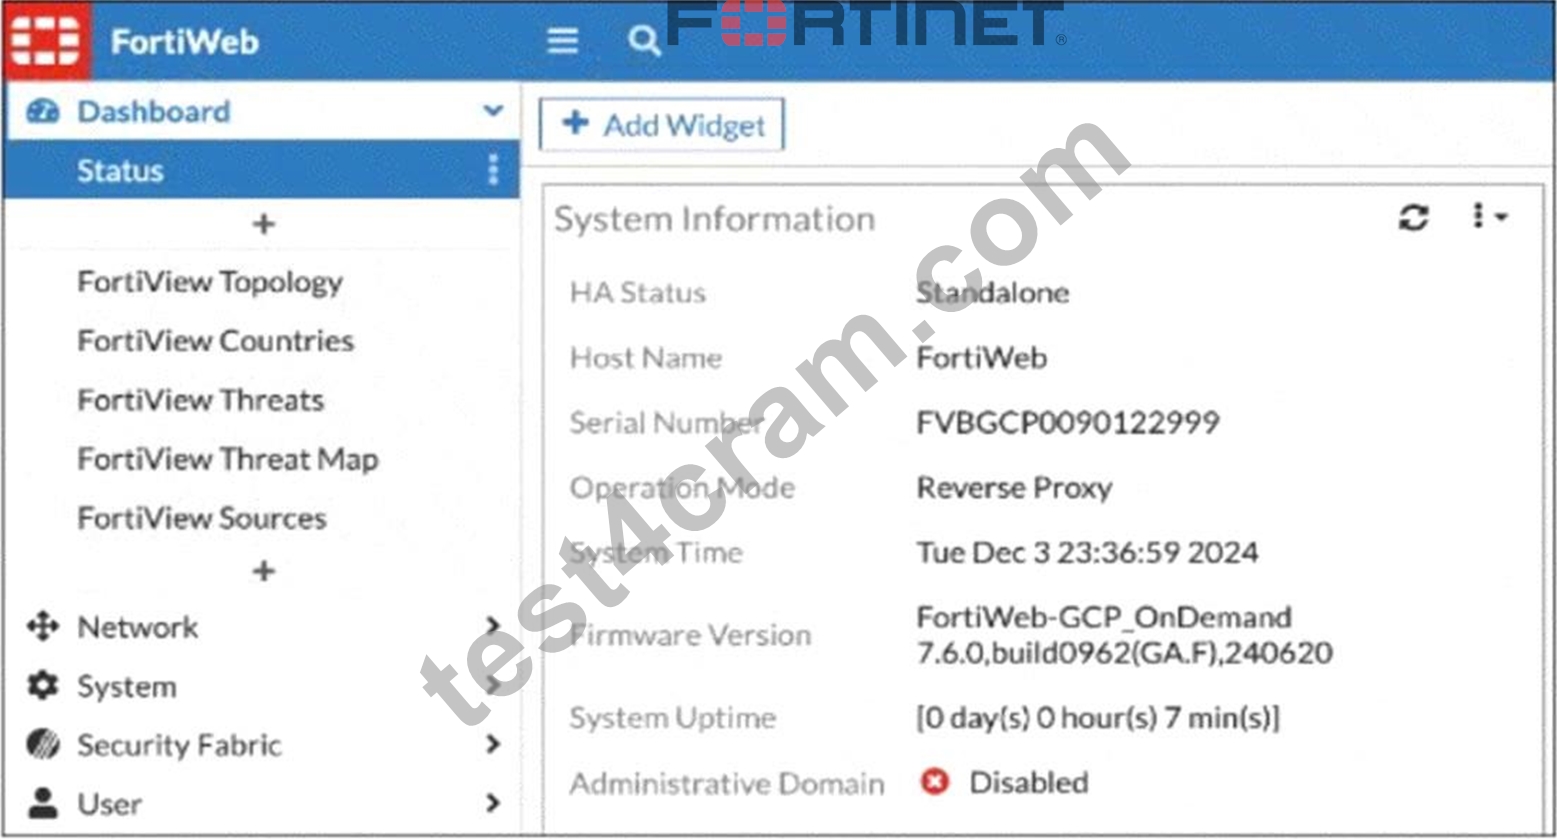
Which two statements about FortiWeb instances deployed in Google Cloud are true?
- A. By default, you can access FortiWeb using HTTPS on port 443.
- B. You can deploy FortiWeb using pay-as-you-go or bring-your-own-license.
- C. You can configure the FortiWeb instance with only one network interface.
- D. You can change the operation mode of FortiWeb.
Answer: B,D
Explanation:
FortiWeb's operation mode can be changed, such as between reverse proxy and transparent modes, to suit different deployment scenarios.
FortiWeb in Google Cloud supports flexible licensing models, including pay-as-you-go and bring-your-own- license (BYOL).
NEW QUESTION # 32
You have been tasked with destroying all resources relating to a recent active-active high-availability (HA) FGSP Terraform deployment in Google Cloud.
What steps do you have to take to ensure a successful deletion? (Choose two.)
- A. Delete all resources manually because active-active HA clusters cannot be destroyed using Terraform.
- B. Use the command terraform plan before destroying the Terraform template.
- C. Use the command terraform destroy to delete all resources deployed by the Terraform template.
- D. Delete all dependencies to resources relating to the Terraform template.
Answer: C,D
Explanation:
Removing dependencies prevents resource conflicts during deletion.
terraform destroy is the correct command to cleanly and completely remove all resources created by the Terraform deployment.
NEW QUESTION # 33
Refer to the exhibit.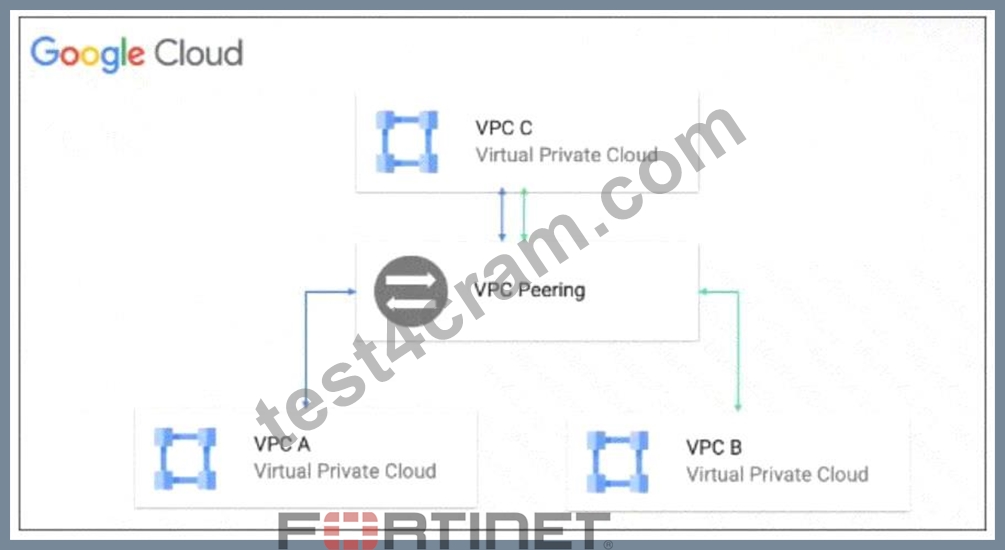
Which action must the administrator take to route traffic from VPC B to VPC A?
- A. The administrator must create a new VPC peering connection between VPC A and VPC B.
- B. The administrator must deploy a FortiGate VM with at least three network interfaces.
- C. The administrator must configure a custom route in VPC B and point the gateway to the VPC peering service.
- D. The administrative must configure a custom route in VPC B and point the gateway to VPC A.
Answer: B
Explanation:
Because VPC peering is non-transitive, traffic cannot route from VPC B to VPC A via VPC C. To enable routing between VPC A and VPC B through VPC C, a FortiGate VM with multiple network interfaces can act as a firewall/router to manage traffic between the three VPCs.
NEW QUESTION # 34
Refer to the exhibit.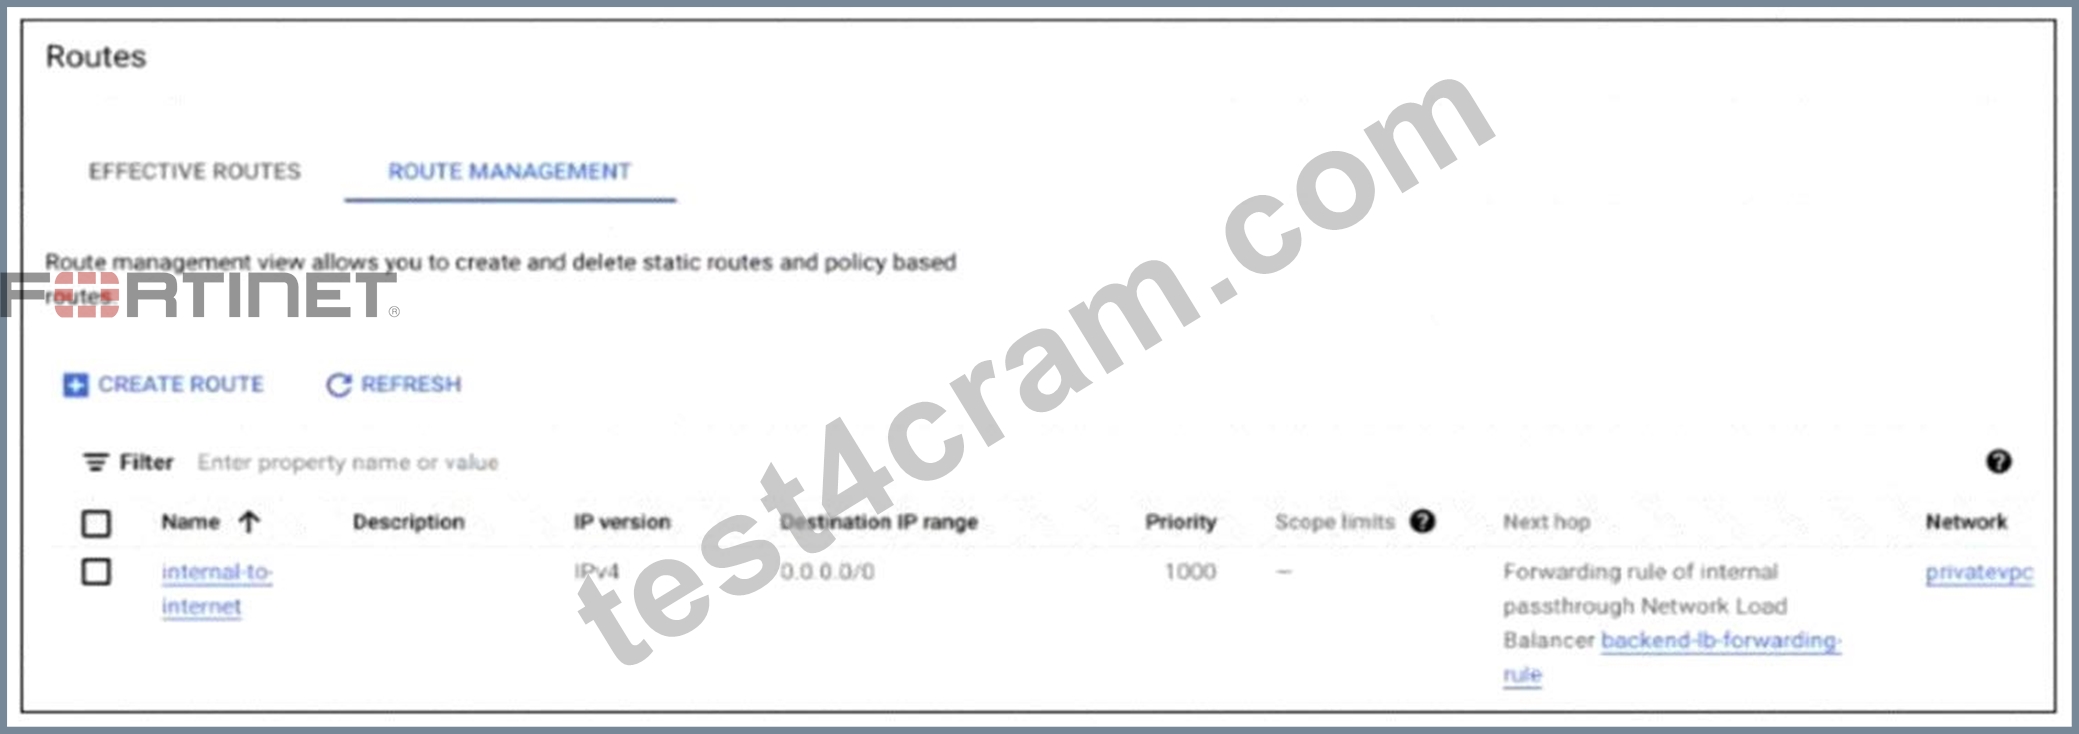
Which three conclusions can you draw from the Google Cloud custom route? (Choose three.)
- A. Atarget pool-based passthrough network load balancer was created.
- B. A group-based passthrough network load balancer was created.
- C. At least one instance group was created.
- D. The next hop must be updates manually in the custom route if the current next hop goes down.
- E. A health check was created.
Answer: C,D,E
Explanation:
The route's next hop is a forwarding rule for a backend service, which indicates a group-based passthrough load balancer.
Group-based load balancers require health checks to monitor instance health.
Backend services attach to instance groups to distribute traffic, so at least one instance group exists.
NEW QUESTION # 35
......
FCP_GCS_AD-7.6 Exam questions and answers: https://www.test4cram.com/FCP_GCS_AD-7.6_real-exam-dumps.html
FCP_GCS_AD-7.6 Actual Questions Answers PDF 100% Cover Real Exam Questions: https://drive.google.com/open?id=1mP83yItPNRfuLO0JqWgNCH5TcKT7F2yD