

2025 Updated Verified Pass SC-200 Study Guides & Best Courses
Ultimate Guide to the SC-200 - Latest Edition Available Now
NEW QUESTION # 57
You plan to connect an external solution that will send Common Event Format (CEF) messages to Azure Sentinel.
You need to deploy the log forwarder.
Which three actions should you perform in sequence? To answer, move the appropriate actions form the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation: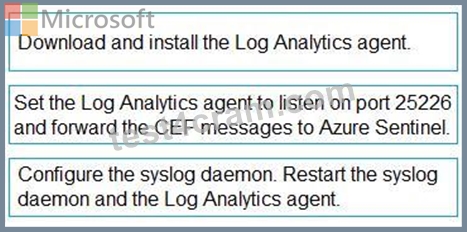
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-cef-agent?tabs=rsyslog
NEW QUESTION # 58
You need to use an Azure Resource Manager template to create a workflow automation that will trigger an automatic remediation when specific security alerts are received by Azure Security Center.
How should you complete the portion of the template that will provision the required Azure resources? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: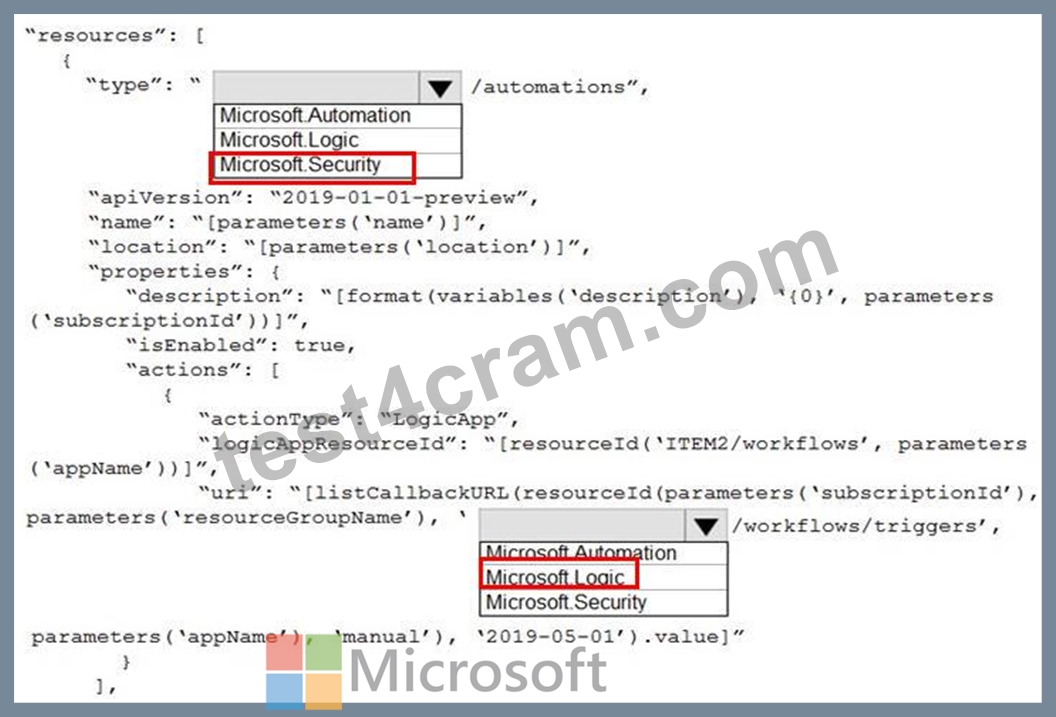
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-automation-alert
NEW QUESTION # 59
You need to recommend remediation actions for the Azure Defender alerts for Fabrikam.
What should you recommend for each threat? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/key-vault/general/secure-your-key-vault
NEW QUESTION # 60
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint.
You need to add threat indicators for all the IP addresses in a range of 171.23.3432-171.2334.63. The solution must minimize administrative effort.
What should you do in the Microsoft 365 Defender portal?
- A. Select Add indicator and set the IP address to
- B. Create an import file that contains the IP address of 171.23.34.32/27. Select Import and import the file.
- C. Create an import file that contains the individual IP addresses in the range. Select Import and import the file.
- D. Select Add indicator and set the IP address to
Answer: C
Explanation:
Explanation
This will add all the IP addresses in the range of 171.23.34.32/27 as threat indicators. This is the simplest and most efficient way to add all the IP addresses in the range.
Reference:
[1] https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/threat-intelligenc
NEW QUESTION # 61
You have a Microsoft 365 subscription
You need to identify all the security principals that submitted requests to change or delete groups. How should you complete the KQL query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.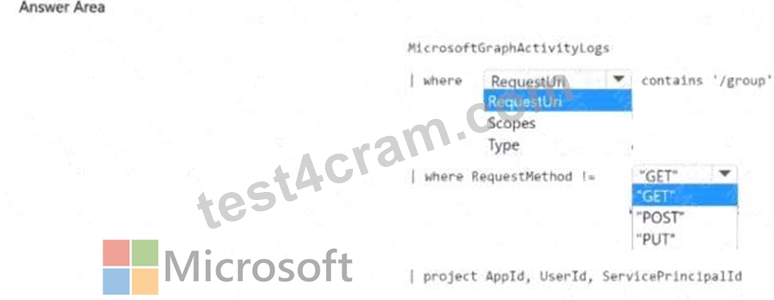
Answer:
Explanation:
Explanation:
NEW QUESTION # 62
You have two Azure subscriptions that use Microsoft Defender for Cloud.
You need to ensure that specific Defender for Cloud security alerts are suppressed at the root management group level. The solution must minimize administrative effort.
What should you do in the Azure portal?
- A. Create an alert rule in Azure Monitor.
- B. Modify the alert settings in Defender for Cloud.
- C. Create an Azure Policy assignment.
- D. Modify the Workload protections settings in Defender for Cloud.
Answer: B
Explanation:
Explanation
You can use alerts suppression rules to suppress false positives or other unwanted security alerts from Defender for Cloud.
Note: To create a rule directly in the Azure portal:
1. From Defender for Cloud's security alerts page:
Select the specific alert you don't want to see anymore, and from the details pane, select Take action.
Or, select the suppression rules link at the top of the page, and from the suppression rules page select Create new suppression rule:
2. In the new suppression rule pane, enter the details of your new rule.
Your rule can dismiss the alert on all resources so you don't get any alerts like this one in the future.
Your rule can dismiss the alert on specific criteria - when it relates to a specific IP address, process name, user account, Azure resource, or location.
3. Enter details of the rule.
4. Save the rule.
Reference: https://docs.microsoft.com/en-us/azure/defender-for-cloud/alerts-suppression-rules
NEW QUESTION # 63
You have an Azure subscription. The subscription contains 10 virtual machines that are onboarded to Microsoft Defender for Cloud.
You need to ensure that when Defender for Cloud detects digital currency mining behavior on a virtual machine, you receive an email notification. The solution must generate a test email.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - From Logic App Designer, Create a logic app.
2 - From Logic App Designer, run a trigger.
3 - From Workflow automation in Defender for cloud, add a workflow automation.
NEW QUESTION # 64
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: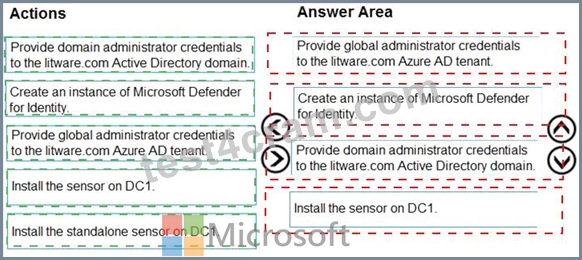
Explanation:
Step 1: log in to https://portal.atp.azure.com as a global admin
Step 2: Create the instance
Step 3. Connect the instance to Active Directory
Step 4. Download and install the sensor.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
Topic 3, Adatum Corporation
Adatum Corporation is a United States-based financial services company that has regional offices in New York, Chicago, and San Francisco.
The on-premises network contains an Active Directory Domain Services (AD DS) forest named corp.adatum.com that syncs with an Azure AD tenant named adatum.com. All user and group management tasks are performed in corp.adatum.com. The corp.adatum.com domain contains a group named Group! that syncs with adatum.com.
All the users at Adatum are assigned a Microsoft 365 E5 license and an Azure Active Directory Perineum 92 license.
The cloud environment contains a Microsoft 365 subscription, an Azure subscription linked to the adatum.com tenant, and the resources shown in the following table.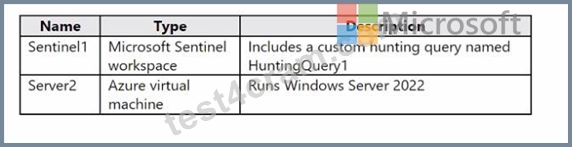
The on-premises network contains the resources shown in the following table.
Adatum plans to perform the following changes;
* Implement a query named rulequery1 that will include the following KQL query.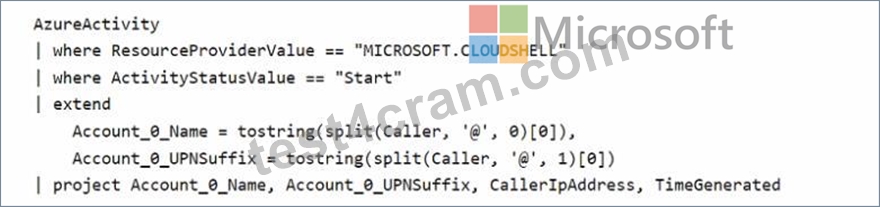
* Implement a Microsoft Sentinel scheduled rule that generates incidents based on rulequery1.
Adatum identifies the following Microsoft Defender for Cloud requirements:
* The members of Group1 must be able to enable Defender for Cloud plans and apply regulatory compliance initiatives.
* Microsoft Defender for Servers Plan 2 must be enabled on all the Azure virtual machines.
* Server2 must be excluded from agentless scanning.
Adatum identifies the following Microsoft Sentinel requirements:
* Implement an Advanced Security Information Model (ASIM) query that will return a count of DNS requests that results in an NXDOMAIN response from Infoblox1.
* Ensure that multiple alerts generated by rulequery1 in response to a single user launching Azure Cloud Shell multiple times are consolidated as a single incident.
* Implement the Windows Security Events via AMA connector for Microsoft Sentinel and configure it to monitor the Security event log of Server1.
* Ensure that incidents generated by rulequery1 are closed automatically if Azure Cloud Shell is launched by the company's SecOps team.
* Implement a custom Microsoft Sentinel workbook named Workbook1 that will include a query to dynamically retrieve data from Webapp1.
* Implement a Microsoft Sentinel near-real-time (NRT) analytics rule that detects sign-ins to a designated break glass account
* Ensure that HuntingQuery1 runs automatically when the Hunting page of Microsoft Sentinel in the Azure portal is accessed.
* Ensure that higher than normal volumes of password resets for corp.adatum.com user accounts are detected.
* Minimize the overhead associated with queries that use ASIM parsers.
* Ensure that the Group1 members can create and edit playbooks.
* Use built-in ASIM parsers whenever possible.
Adatum identifies the following business requirements:
* Follow the principle of least privilege whenever possible.
* Minimize administrative effort whenever possible.
Directory Perineum 92 license.
NEW QUESTION # 65
You have a Microsoft Sentinel workspace named workspace1 and an Azure virtual machine named VM1.
You receive an alert for suspicious use of PowerShell on VM1.
You need to investigate the incident, identify which event triggered the alert, and identify whether the following actions occurred on VM1 after the alert:
* The modification of local group memberships
* The purging of event logs
Which three actions should you perform in sequence in the Azure portal? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.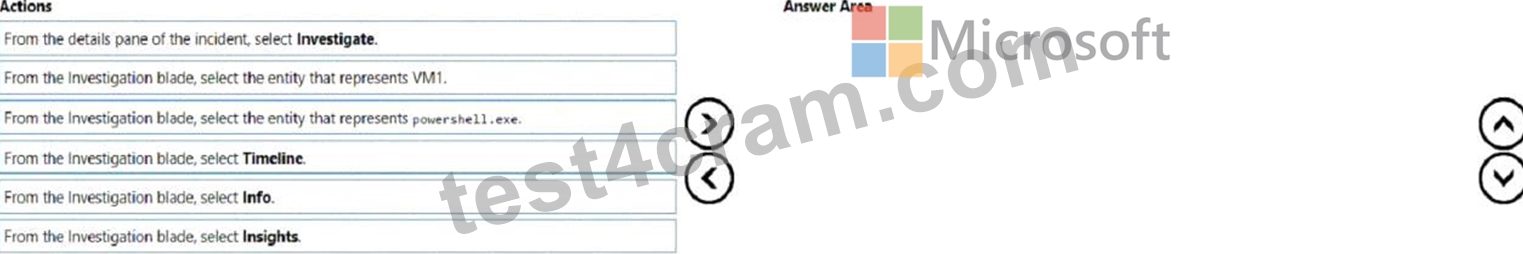
Answer:
Explanation:
Explanation:
Step 1: From the Investigation blade, select Insights
The Investigation Insights Workbook is designed to assist in investigations of Azure Sentinel Incidents or individual IP/Account/Host/URL entities.
Step 2: From the Investigation blade, select the entity that represents VM1.
The Investigation Insights workbook is broken up into 2 main sections, Incident Insights and Entity Insights.
Incident Insights
The Incident Insights gives the analyst a view of ongoing Sentinel Incidents and allows for quick access to their associated metadata including alerts and entity information.
Entity Insights
The Entity Insights allows the analyst to take entity data either from an incident or through manual entry and explore related information about that entity. This workbook presently provides view of the following entity types:
IP Address
Account
Host
URL
Step 3: From the details pane of the incident, select Investigate.
Choose a single incident and click View full details or Investigate.
Reference:
https://github.com/Azure/Azure-Sentinel/wiki/Investigation-Insights---Overview
https://docs.microsoft.com/en-us/azure/sentinel/investigate-cases
NEW QUESTION # 66
You have a suppression rule in Azure Security Center for 10 virtual machines that are used for testing. The virtual machines run Windows Server.
You are troubleshooting an issue on the virtual machines.
In Security Center, you need to view the alerts generated by the virtual machines during the last five days.
What should you do?
- A. View the Windows event logs on the virtual machines.
- B. Change the rule expiration date of the suppression rule.
- C. Modify the filter for the Security alerts page.
- D. Change the state of the suppression rule to Disabled.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/alerts-suppression-rules
NEW QUESTION # 67
You need to implement the Azure Information Protection requirements.
What should you configure first?
- A. scanner clusters in Azure Information Protection from the Azure portal
- B. Device health and compliance reports settings in Microsoft Defender Security Center
- C. content scan jobs in Azure Information Protection from the Azure portal
- D. Advanced features from Settings in Microsoft Defender Security Center
Answer: D
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/information- protection-in-windows-overview
NEW QUESTION # 68
You have a Microsoft Sentinel workspace named sws1.
You plan to create an Azure logic app that will raise an incident in an on-premises IT service management system when an incident is generated in sws1.
You need to configure the Microsoft Sentinel connector credentials for the logic app. The solution must meet the following requirements:
* Minimize administrative effort.
* Use the principle of least privilege.
How should you configure the credentials? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 69
You have an Azure subscription that contains a Microsoft Sentinel workspace named WS1.
You create a hunting query that detects a new attack vector. The attack vector maps to a tactic listed in the MITRE ATT&CK database.
You need to ensure that an incident is created in WS1 when the new attack vector is detected.
What should you configure?
- A. a hunting livestream session
- B. a query bookmark
- C. a scheduled query rule
- D. a Fusion rule
Answer: C
NEW QUESTION # 70
You need to remediate active attacks to meet the technical requirements.
What should you include in the solution?
- A. Azure Functions
- B. Azure Logic Apps
- C. Azure Automation runbooks
Answer: B
Explanation:
D Azure Sentinel livestreams
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/automate-responses-with-playbooks
NEW QUESTION # 71
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Azure Sentinel.
You need to create an incident in Azure Sentinel when a sign-in to an Azure virtual machine from a malicious IP address is detected.
Solution: You create a hunting bookmark.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-azure-security-center
NEW QUESTION # 72
You need to implement the Microsoft Sentinel NRT rule for monitoring the designated break glass account. The solution must meet the Microsoft Sentinel requirements.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.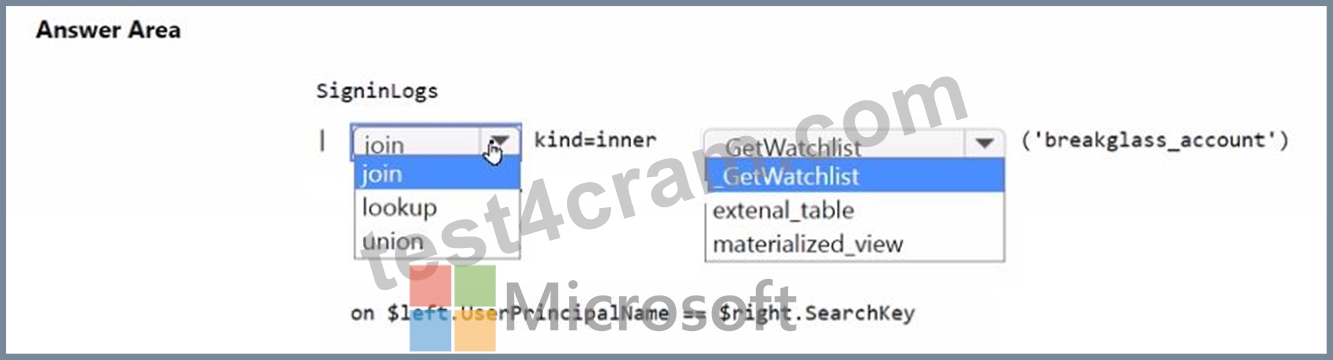
Answer:
Explanation:
NEW QUESTION # 73
You need to implement Azure Sentinel queries for Contoso and Fabrikam to meet the technical requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/extend-sentinel-across-workspaces-tenants
NEW QUESTION # 74
You have a Microsoft 365 E5 subscription that uses Microsoft Defender and an Azure subscription that uses Azure Sentinel.
You need to identify all the devices that contain files in emails sent by a known malicious email sender. The query will be based on the match of the SHA256 hash.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: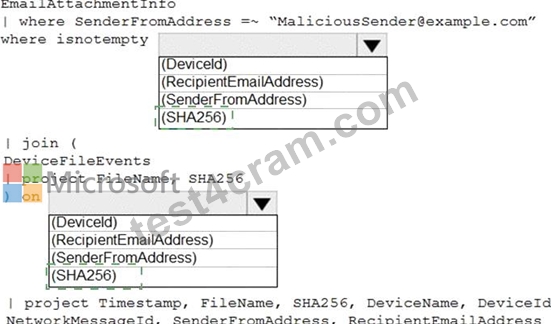
Explanation
Graphical user interface, text, application Description automatically generated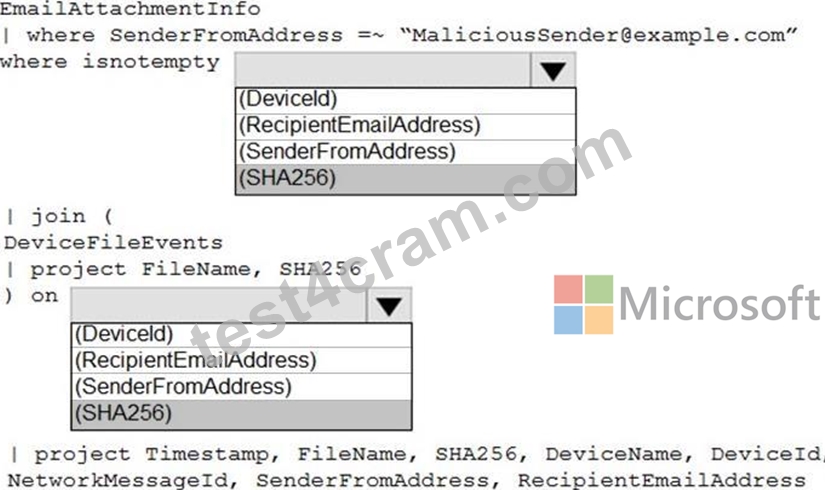
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/advanced-hunting-query-emails-devices?view=
NEW QUESTION # 75
You are informed of a new common vulnerabilities and exposures (CVE) vulnerability that affects your environment.
You need to use Microsoft Defender Security Center to request remediation from the team responsible for the affected systems if there is a documented active exploit available.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - From Threat & Vulnerabilty Management, select Weaknesess, and search fot the CVE.
2 - Select Security recommendations.
3 - Create the remediation request.
Reference:
https://techcommunity.microsoft.com/t5/core-infrastructure-and-security/microsoft-defender-atp-remediate-apps-using-mem/ba-p/1599271
NEW QUESTION # 76
You have an Azure subscription that contains an Microsoft Sentinel workspace.
You need to create a hunting query using Kusto Query Language (KQL) that meets the following requirements:
* Identifies an anomalous number of changes to the rules of a network security group (NSG) made by the same security principal
* Automatically associates the security principal with an Microsoft Sentinel entity How should you complete the query? To answer, select the appropriate options in the answer area. NOTE:
Each correct selection is worth one point.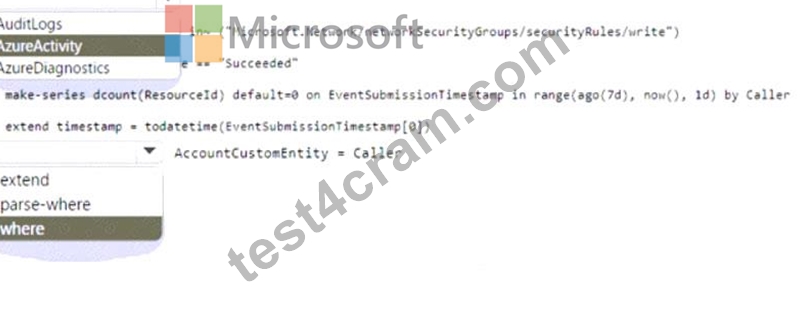
Answer:
Explanation:
NEW QUESTION # 77
You have a Microsoft Sentinel workspace that contains a custom workbook.
You need to query the number of daily security alerts. The solution must meet the following requirements:
* Identify alerts that occurred during the last 30 days.
* Display the results in a timechart.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE:
Each correct selection is worth one point.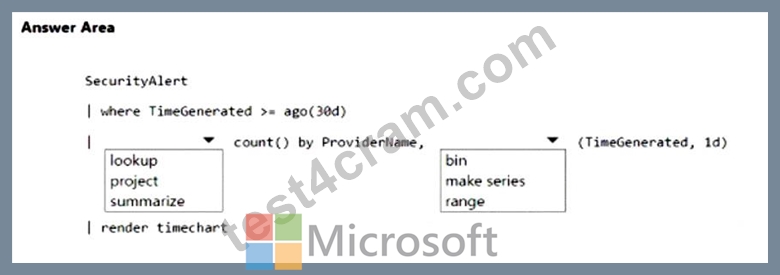
Answer:
Explanation:
Explanation:
NEW QUESTION # 78
......
Dumps MoneyBack Guarantee - SC-200 Dumps Approved Dumps: https://www.test4cram.com/SC-200_real-exam-dumps.html
2025 Updated Verified Pass SC-200 Exam - Real Questions and Answers: https://drive.google.com/open?id=13Tpx-RP9Ps0EvLuA3qm2N2YtOIhyGNUt