

Microsoft New 2022 SC-200 Sample Questions Reliable SC-200 Test Engine
Feel Microsoft SC-200 Dumps PDF Will likely be The best Option
NEW QUESTION 19
The issue for which team can be resolved by using Microsoft Defender for Endpoint?
- A. executive
- B. sales
- C. marketing
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/microsoft-defender-atp-ios
NEW QUESTION 20
You have an existing Azure logic app that is used to block Azure Active Directory (Azure AD) users. The logic app is triggered manually.
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel.
What should you do first?
- A. And a new scheduled query rule.
- B. Add a data connector to Azure Sentinel.
- C. Configure a custom Threat Intelligence connector in Azure Sentinel.
- D. Modify the trigger in the logic app.
Answer: B
Explanation:
Explanation/Reference:
NEW QUESTION 21
You need to create the test rule to meet the Azure Sentinel requirements.
What should you do when you create the rule?
- A. From Set rule logic, map the entities.
- B. From Analytics rule details, configure the severity.
- C. From Analytics rule details, configure the tactics.
- D. From Set rule logic, turn off suppression.
Answer: A
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-detect-threats-custom
NEW QUESTION 22
You need to create the analytics rule to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 23
DRAG DROP
You need to add notes to the events to meet the Azure Sentinel requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.
Select and Place: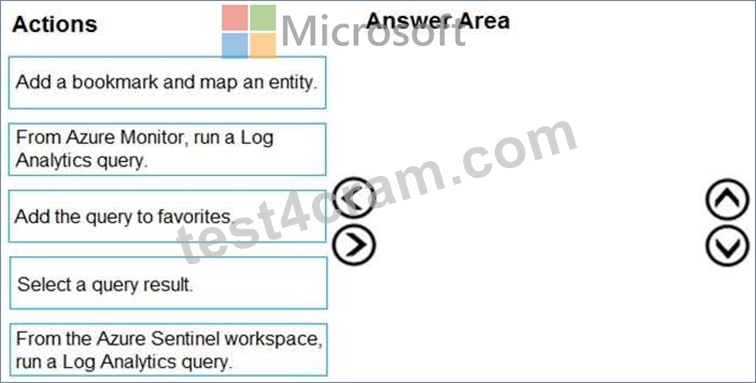
Answer:
Explanation: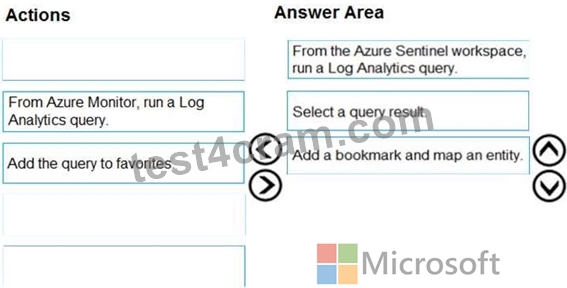
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/bookmarks
NEW QUESTION 24
You need to implement the Azure Information Protection requirements. What should you configure first?
- A. scanner clusters in Azure Information Protection from the Azure portal
- B. Advanced features from Settings in Microsoft Defender Security Center
- C. content scan jobs in Azure Information Protection from the Azure portal
- D. Device health and compliance reports settings in Microsoft Defender Security Center
Answer: B
Explanation:
Explanation
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/information- protection-in-windows-overview
NEW QUESTION 25
You have a custom analytics rule to detect threats in Azure Sentinel.
You discover that the analytics rule stopped running. The rule was disabled, and the rule name has a prefix of AUTO DISABLED.
What is a possible cause of the issue?
- A. The rule query takes too long to run and times out.
- B. There are connectivity issues between the data sources and Log Analytics.
- C. Permissions to one of the data sources of the rule query were modified.
- D. The number of alerts exceeded 10,000 within two minutes.
Answer: C
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-detect-threats-custom
NEW QUESTION 26
You have a Microsoft 365 E5 subscription.
You plan to perform cross-domain investigations by using Microsoft 365 Defender.
You need to create an advanced hunting query to identify devices affected by a malicious email attachment.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/mtp/advanced-hunting-query-emails-devices?view=o365-worldwide
NEW QUESTION 27
You use Azure Sentinel.
You need to use a built-in role to provide a security analyst with the ability to edit the queries of custom Azure Sentinel workbooks. The solution must use the principle of least privilege.
Which role should you assign to the analyst?
- A. Azure Sentinel Responder
- B. Security Administrator
- C. Azure Sentinel Contributor
- D. Logic App Contributor
Answer: C
Explanation:
Azure Sentinel Contributor can create and edit workbooks, analytics rules, and other Azure Sentinel resources.
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/roles
NEW QUESTION 28
HOTSPOT
You need to recommend remediation actions for the Azure Defender alerts for Fabrikam.
What should you recommend for each threat? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: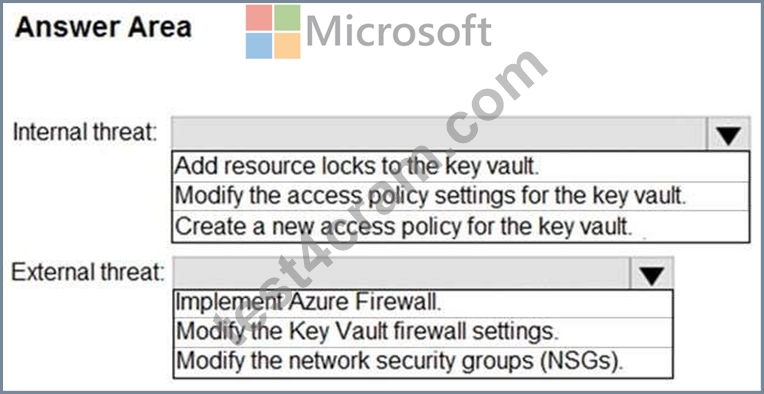
Answer:
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/key-vault/general/security-features
https://docs.microsoft.com/en-us/azure/key-vault/general/secure-your-key-vault
NEW QUESTION 29
The issue for which team can be resolved by using Microsoft Defender for Endpoint?
- A. executive
- B. sales
- C. marketing
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/microsoft-defender-atp-ios
Topic 2, Litware inc.
Overview
Litware Inc. is a renewable company.
Litware has offices in Boston and Seattle. Litware also has remote users located across the United States. To access Litware resources, including cloud resources, the remote users establish a VPN connection to either office.
Existing Environment
Identity Environment
The network contains an Active Directory forest named litware.com that syncs to an Azure Active Directory (Azure AD) tenant named litware.com.
Microsoft 365 Environment
Litware has a Microsoft 365 E5 subscription linked to the litware.com Azure AD tenant. Microsoft Defender for Endpoint is deployed to all computers that run Windows 10. All Microsoft Cloud App Security built-in anomaly detection policies are enabled.
Azure Environment
Litware has an Azure subscription linked to the litware.com Azure AD tenant. The subscription contains resources in the East US Azure region as shown in the following table.
Network Environment
Each Litware office connects directly to the internet and has a site-to-site VPN connection to the virtual networks in the Azure subscription.
On-premises Environment
The on-premises network contains the computers shown in the following table.
Current problems
Cloud App Security frequently generates false positive alerts when users connect to both offices simultaneously.
Planned Changes
Litware plans to implement the following changes:
Create and configure Azure Sentinel in the Azure subscription.
Validate Azure Sentinel functionality by using Azure AD test user accounts.
Business Requirements
Litware identifies the following business requirements:
* Azure Information Protection Requirements
* All files that have security labels and are stored on the Windows 10 computers must be available from the Azure Information * Protection - Data discovery dashboard.
* Microsoft Defender for Endpoint Requirements
All Cloud App Security unsanctioned apps must be blocked on the Windows 10 computers by using Microsoft Defender for Endpoint.
Microsoft Cloud App Security Requirements
Cloud App Security must identify whether a user connection is anomalous based on tenant-level data.
Azure Defender Requirements
All servers must send logs to the same Log Analytics workspace.
Azure Sentinel Requirements
Litware must meet the following Azure Sentinel requirements:
Integrate Azure Sentinel and Cloud App Security.
Ensure that a user named admin1 can configure Azure Sentinel playbooks.
Create an Azure Sentinel analytics rule based on a custom query. The rule must automatically initiate the execution of a playbook.
Add notes to events that represent data access from a specific IP address to provide the ability to reference the IP address when navigating through an investigation graph while hunting.
Create a test rule that generates alerts when inbound access to Microsoft Office 365 by the Azure AD test user accounts is detected. Alerts generated by the rule must be grouped into individual incidents, with one incident per test user account.
NEW QUESTION 30
You are investigating an incident by using Microsoft 365 Defender.
You need to create an advanced hunting query to detect failed sign-in authentications on three devices named CFOLaptop, CEOLaptop, and COOLaptop.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.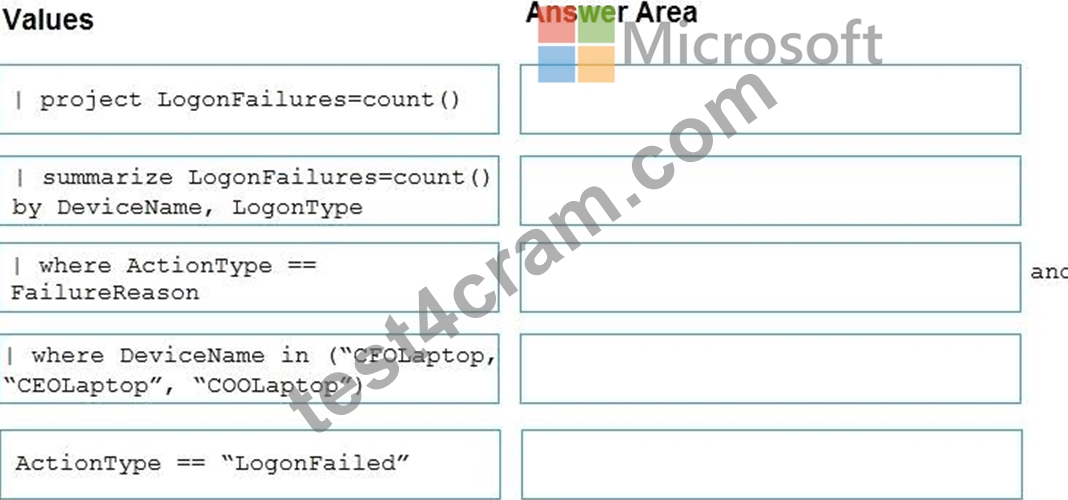
Answer:
Explanation: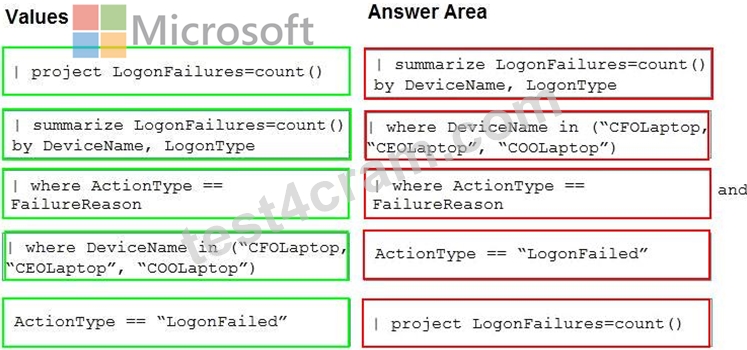
NEW QUESTION 31
You implement Safe Attachments policies in Microsoft Defender for Office 365.
Users report that email messages containing attachments take longer than expected to be received.
You need to reduce the amount of time it takes to deliver messages that contain attachments without compromising security. The attachments must be scanned for malware, and any messages that contain malware must be blocked.
What should you configure in the Safe Attachments policies?
- A. Monitor and Enable redirect
- B. Replace
- C. Block and Enable redirect
- D. Dynamic Delivery
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/safe-attachments?view=o365-world
NEW QUESTION 32
DRAG DROP
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation:
Section: [none]
Explanation:
Step 1: log in to https://portal.atp.azure.com as a global admin
Step 2: Create the instance
Step 3. Connect the instance to Active Directory
Step 4. Download and install the sensor.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
Question Set 3
NEW QUESTION 33
Your company deploys the following services:
* Microsoft Defender for Identity
* Microsoft Defender for Endpoint
* Microsoft Defender for Office 365
You need to provide a security analyst with the ability to use the Microsoft 365 security center. The analyst must be able to approve and reject pending actions generated by Microsoft Defender for Endpoint. The solution must use the principle of least privilege.
Which two roles should assign to the analyst? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. the Security Administrator role in Azure Active Directory (Azure AD)
- B. the Security Reader role in Azure Active Directory (Azure AD)
- C. the Compliance Data Administrator in Azure Active Directory (Azure AD)
- D. the Active remediation actions role in Microsoft Defender for Endpoint
Answer: B,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/rbac?view=o365-worldwide
NEW QUESTION 34
Your company uses Azure Sentinel to manage alerts from more than 10,000 IoT devices.
A security manager at the company reports that tracking security threats is increasingly difficult due to the large number of incidents.
You need to recommend a solution to provide a custom visualization to simplify the investigation of threats and to infer threats by using machine learning.
What should you include in the recommendation?
- A. bookmarks
- B. livestream
- C. notebooks
- D. built-in queries
Answer: C
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/notebooks
NEW QUESTION 35
You are investigating a potential attack that deploys a new ransomware strain.
You plan to perform automated actions on a group of highly valuable machines that contain sensitive information.
You have three custom device groups.
You need to be able to temporarily group the machines to perform actions on the devices. Which three actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Add the device users to the admin role.
- B. Create a new admin role.
- C. Add a tag to the device group.
- D. Create a new device group that has a rank of 4.
- E. Add a tag to the machines.
- F. Create a new device group that has a rank of 1.
Answer: C,E,F
Explanation:
https://docs.microsoft.com/en-us/learn/modules/deploy-microsoft-defender-for-endpoints-environment/4-manage-access
NEW QUESTION 36
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Provide global administrator credentials to the litware.com Azure AD tenant.
2 - Create an instance of Microsoft Defender for Identity.
3 - Provide domain administrator credentials to the litware.com Active Directory domain.
4 - Install the sensor on DC1.
Explanation:
Step 1: log in to https://portal.atp.azure.com as a global admin
Step 2: Create the instance
Step 3. Connect the instance to Active Directory
Step 4. Download and install the sensor.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
NEW QUESTION 37
You use Azure Defender.
You have an Azure Storage account that contains sensitive information.
You need to run a PowerShell script if someone accesses the storage account from a suspicious IP address.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create an Azure logic app that has an Azure Security Center alert trigger.
- B. Create an Azure logic app that has a manual trigger.
- C. From Azure Security Center, enable workflow automation.
- D. From Azure Active Directory (Azure AD), add an app registration.
- E. Create an Azure logic app that has an HTTP trigger.
Answer: A,C
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/storage/common/azure-defender-storage-configure?tabs=azure- security-center
https://docs.microsoft.com/en-us/azure/security-center/workflow-automation Testlet 1 Case study This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam.
You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
A company named Contoso Ltd. has a main office and five branch offices located throughout North America.
The main office is in Seattle. The branch offices are in Toronto, Miami, Houston, Los Angeles, and Vancouver.
Contoso has a subsidiary named Fabrikam, Ltd. that has offices in New York and San Francisco.
Existing Environment
End-User Environment
All users at Contoso use Windows 10 devices. Each user is licensed for Microsoft 365. In addition, iOS devices are distributed to the members of the sales team at Contoso.
Cloud and Hybrid Infrastructure
All Contoso applications are deployed to Azure.
You enable Microsoft Cloud App Security.
Contoso and Fabrikam have different Azure Active Directory (Azure AD) tenants. Fabrikam recently purchased an Azure subscription and enabled Azure Defender for all supported resource types.
Current Problems
The security team at Contoso receives a large number of cybersecurity alerts. The security team spends too much time identifying which cybersecurity alerts are legitimate threats, and which are not.
The Contoso sales team uses only iOS devices. The sales team members exchange files with customers by using a variety of third-party tools. In the past, the sales team experienced various attacks on their devices.
The marketing team at Contoso has several Microsoft SharePoint Online sites for collaborating with external vendors. The marketing team has had several incidents in which vendors uploaded files that contain malware.
The executive team at Contoso suspects a security breach. The executive team requests that you identify which files had more than five activities during the past 48 hours, including data access, download, or deletion for Microsoft Cloud App Security-protected applications.
Requirements
Planned Changes
Contoso plans to integrate the security operations of both companies and manage all security operations centrally.
Technical Requirements
Contoso identifies the following technical requirements:
* Receive alerts if an Azure virtual machine is under brute force attack.
* Use Azure Sentinel to reduce organizational risk by rapidly remediating active attacks on the environment.
* Implement Azure Sentinel queries that correlate data across the Azure AD tenants of Contoso and Fabrikam.
* Develop a procedure to remediate Azure Defender for Key Vault alerts for Fabrikam in case of external attackers and a potential compromise of its own Azure AD applications.
* Identify all cases of users who failed to sign in to an Azure resource for the first time from a given country. A junior security administrator provides you with the following incomplete query.
BehaviorAnalytics
| where ActivityType == "FailedLogOn"
| where ________ == True
NEW QUESTION 38
You use Azure Security Center.
You receive a security alert in Security Center.
You need to view recommendations to resolve the alert in Security Center.
What should you do?
- A. From Security alerts, select Take Action, and then expand the Mitigate the threat section.
- B. From Recommendations, download the CSV report.
- C. From Regulatory compliance, download the report.
- D. From Security alerts, select the alert, select Take Action, and then expand the Prevent future attacks section.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-managing-and-responding-alerts
NEW QUESTION 39
You have the following advanced hunting query in Microsoft 365 Defender.
You need to receive an alert when any process disables System Restore on a device managed by Microsoft Defender during the last 24 hours.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Replace DeviceProcessEventswith DeviceNetworkEvents.
- B. Create a detection rule.
- C. Add | orderby Timestamp to the query.
- D. Add DeviceIdand ReportIdto the output of the query.
- E. Create a suppression rule.
Answer: B,D
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/custom-detection- rules
NEW QUESTION 40
Your company deploys Azure Sentinel.
You plan to delegate the administration of Azure Sentinel to various groups.
You need to delegate the following tasks:
Create and run playbooks
Create workbooks and analytic rules.
The solution must use the principle of least privilege.
Which role should you assign for each task? To answer, drag the appropriate roles to the correct tasks. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/roles
NEW QUESTION 41
You need to implement the Azure Information Protection requirements.
What should you configure first?
- A. scanner clusters in Azure Information Protection from the Azure portal
- B. Advanced features from Settings in Microsoft Defender Security Center
- C. content scan jobs in Azure Information Protection from the Azure portal
- D. Device health and compliance reports settings in Microsoft Defender Security Center
Answer: B
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/information- protection-in-windows-overview
NEW QUESTION 42
......
Use Valid New SC-200 Test Notes & SC-200 Valid Exam Guide: https://www.test4cram.com/SC-200_real-exam-dumps.html
SC-200 exam torrent Microsoft study guide: https://drive.google.com/open?id=1u8gmc0DGDX0tTiP1jHAnDOmMluwIehtx