

225 Exam Questions for SC-200 Updated Versions With Test Engine
Pass SC-200 Exam with Updated SC-200 Exam Dumps PDF 2023
Microsoft SC-200 exam is ideal for individuals who want to advance their careers in the cybersecurity industry. Microsoft Security Operations Analyst certification is intended for security analysts, security administrators, and other IT professionals who are responsible for monitoring, analyzing, and responding to security incidents. Additionally, the exam is suitable for individuals who want to demonstrate their expertise in Microsoft security technologies.
NEW QUESTION # 58
You need to complete the query for failed sign-ins to meet the technical requirements.
Where can you find the column name to complete the where clause?
- A. Azure Advisor
- B. the query windows of the Log Analytics workspace
- C. Security alerts in Azure Security Center
- D. Activity log in Azure
Answer: B
NEW QUESTION # 59
A company wants to analyze by using Microsoft 365 Apps.
You need to describe the connected experiences the company can use.
Which connected experiences should you describe? To answer, drag the appropriate connected experiences to the correct description. Each connected experience may be used once, more than once, or not at all. You may need to drag the split between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 60
You need to use an Azure Resource Manager template to create a workflow automation that will trigger an automatic remediation when specific security alerts are received by Azure Security Center.
How should you complete the portion of the template that will provision the required Azure resources? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-automation-alert
NEW QUESTION # 61
You need to create the analytics rule to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 62
Your company deploys Azure Sentinel.
You plan to delegate the administration of Azure Sentinel to various groups.
You need to delegate the following tasks:
Create and run playbooks
Create workbooks and analytic rules.
The solution must use the principle of least privilege.
Which role should you assign for each task? To answer, drag the appropriate roles to the correct tasks. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: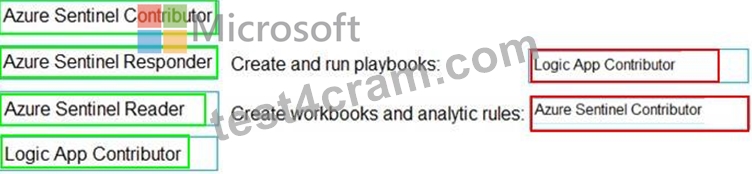
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/roles
NEW QUESTION # 63
You have a Microsoft 365 E5 subscription that uses Microsoft Defender and an Azure subscription that uses Azure Sentinel.
You need to identify all the devices that contain files in emails sent by a known malicious email sender. The query will be based on the match of the SHA256 hash.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.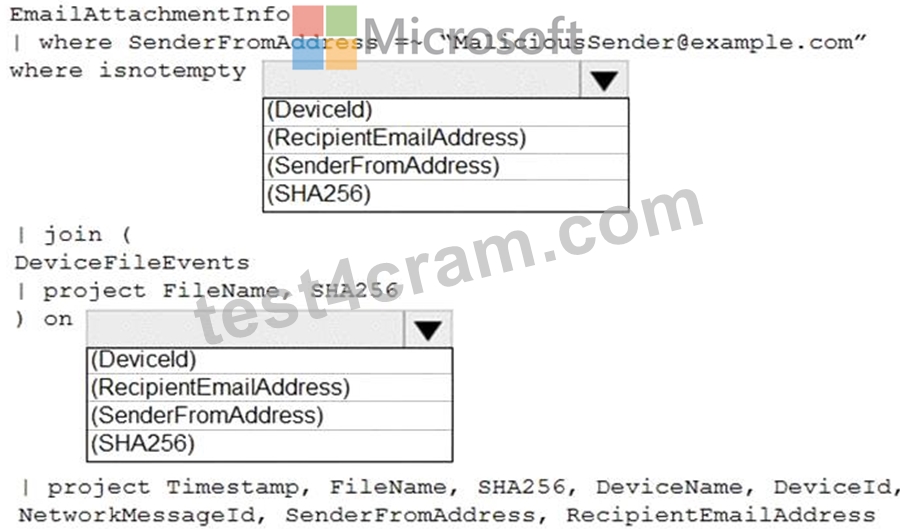
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated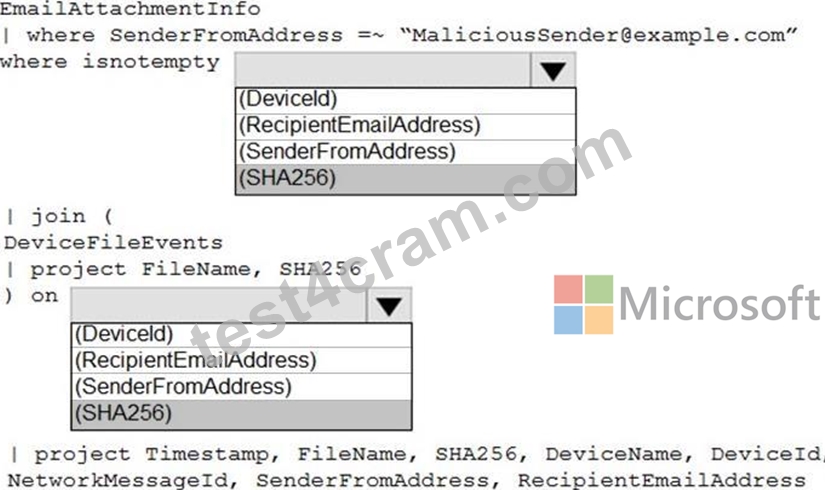
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/advanced-hunting-query-emails-devices?view=
NEW QUESTION # 64
You provision Azure Sentinel for a new Azure subscription. You are configuring the Security Events connector.
While creating a new rule from a template in the connector, you decide to generate a new alert for every event. You create the following rule query.
By which two components can you group alerts into incidents? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. computer
- B. resource group
- C. user
- D. IP address
Answer: A,C
NEW QUESTION # 65
You have the following KQL query.

Answer:
Explanation:
NEW QUESTION # 66
You are investigating a potential attack that deploys a new ransomware strain.
You plan to perform automated actions on a group of highly valuable machines that contain sensitive information.
You have three custom device groups.
You need to be able to temporarily group the machines to perform actions on the devices.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create a new device group that has a rank of 1.
- B. Create a new device group that has a rank of 4.
- C. Add the device users to the admin role.
- D. Create a new admin role.
- E. Add a tag to the device group.
- F. Add a tag to the machines.
Answer: A,C,D
Explanation:
Explanation/Reference:
https://www.drware.com/how-to-use-tagging-effectively-in-microsoft-defender-for-endpoint-part-1/
NEW QUESTION # 67
You need to correlate data from the SecurityEvent Log Anarytks table to meet the Microsoft Sentinel requirements for using UEBA.
Which Log Analytics table should you use?
- A. SentwlAuoNt
- B. Identityinfo
- C. IdentityOirectoryEvents
- D. AADRiskyUsers
Answer: C
NEW QUESTION # 68
You have a Microsoft 365 E5 subscription that uses Microsoft Defender and an Azure subscription that uses Azure Sentinel.
You need to identify all the devices that contain files in emails sent by a known malicious email sender. The query will be based on the match of the SHA256 hash.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.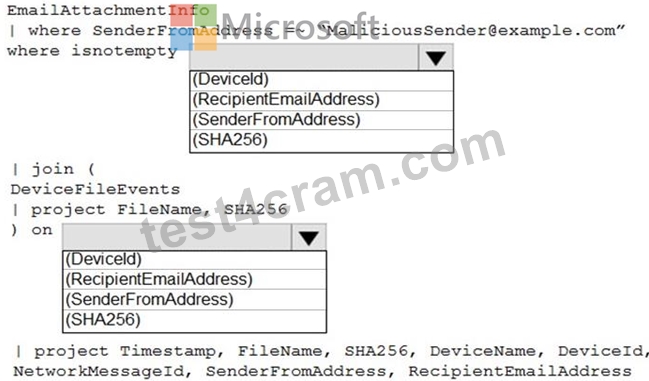
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/advanced-hunting-query-emails-devices?view=o365-worldwide
NEW QUESTION # 69
You have resources in Azure and Google cloud.
You need to ingest Google Cloud Platform (GCP) data into Azure Defender.
In which order should you perform the actions? To answer, move all actions from the list of actions to the answer area and arrange them in the correct order.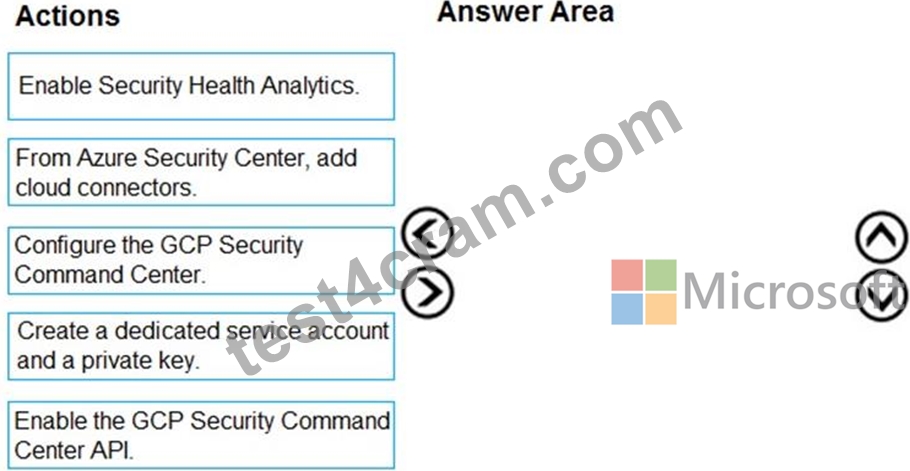
Answer:
Explanation:
1 - Configure the GCP Security Command Center.
2 - Enable Security Health Analytics.
3 - Enable the GCP Security Command Center API.
4 - Create a dedicated service account and a private key.
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-onboard-gcp
NEW QUESTION # 70
You need to create the analytics rule to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 71
You are informed of an increase in malicious email being received by users.
You need to create an advanced hunting query in Microsoft 365 Defender to identify whether the accounts of the email recipients were compromised. The query must return the most recent 20 sign-ins performed by the recipients within an hour of receiving the known malicious email.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/advanced-hunting-query-emails-devices?view=o365-worldwide
NEW QUESTION # 72
You have an Azure subscription that uses Azure Defender.
You plan to use Azure Security Center workflow automation to respond to Azure Defender threat alerts.
You need to create an Azure policy that will perform threat remediation automatically.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/governance/policy/concepts/effects
https://docs.microsoft.com/en-us/azure/security-center/workflow-automation
NEW QUESTION # 73
You need to use an Azure Sentinel analytics rule to search for specific criteria in Amazon Web Services (AWS) logs and to generate incidents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Add the Amazon Web Services connector
2 - From Analytics in Azure Sentinel, create a custom analytics rule ....
3 - Set the alert logic
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/detect-threats-custom
NEW QUESTION # 74
Your network contains an on-premises Active Directory Domain Services (AD DS) domain that syncs with Azure AD.
You have a Microsoft 365 E5 subscription that uses Microsoft Defender 365.
You need to identify all the interactive authentication attempts by the users in the finance department of your company.
How should you complete the KQL query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 75
You have an Azure subscription.
You need to delegate permissions to meet the following requirements:
Enable and disable Azure Defender.
Apply security recommendations to resource.
The solution must use the principle of least privilege.
Which Azure Security Center role should you use for each requirement? To answer, drag the appropriate roles to the correct requirements. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: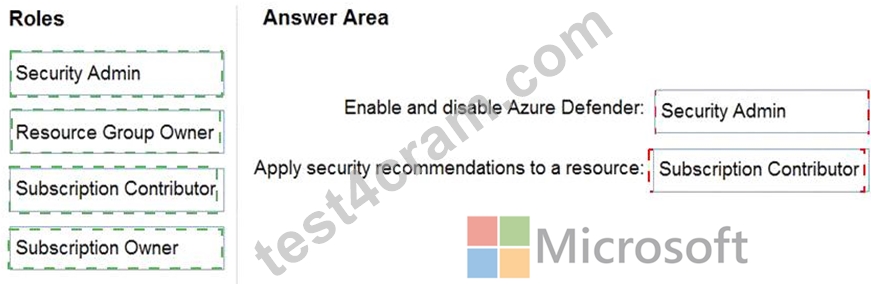
Explanation
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-permissions
NEW QUESTION # 76
You have an Azure Sentinel workspace.
You need to test a playbook manually in the Azure portal.
From where can you run the test in Azure Sentinel?
- A. Playbooks
- B. Analytics
- C. Threat intelligence
- D. Incidents
Answer: D
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook#run-a-playbook-on-demand
NEW QUESTION # 77
You need to implement Azure Sentinel queries for Contoso and Fabrikam to meet the technical requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/extend-sentinel-across-workspaces-tenants
NEW QUESTION # 78
You have a Microsoft 365 subscription. The subscription uses Microsoft 365 Defender and has data loss prevention (DLP) policies that have aggregated alerts configured.
You need to identify the impacted entities in an aggregated alert.
What should you review in the DIP alert management dashboard of the Microsoft Purview compliance portal?
- A. Management log
- B. the Sensitive Info Types tab of the alert
- C. the Details tab of the alert
- D. the Events tab of the alert
Answer: A
NEW QUESTION # 79
......
Microsoft SC-200 certification exam is designed for security operations analysts who want to validate their skills in protecting an organization's assets, detecting and responding to security incidents, and implementing security controls. SC-200 exam is part of the Microsoft Certified: Security Operations Analyst Associate certification, which also includes the SC-900 Fundamentals exam. The SC-200 exam measures your ability to use Microsoft security technologies to identify and respond to security threats.
SC-200 Exam Dumps - Free Demo & 365 Day Updates: https://www.test4cram.com/SC-200_real-exam-dumps.html
Free Sales Ending Soon - Use Real SC-200 PDF Questions: https://drive.google.com/open?id=1bgSvjd-0JhaUiONgTYcvRoBs3hPcIohx